
In October 2026, the financially motivated threat actor Storm-3358 began targeting organizations in the financial sector using the agentic AI
Vendor announcements
Turning Up the Heat: Inside the Attacks on Europe’s Refrigeration System
Unit 42 examines recent cyberattacks targeting European refrigeration systems and outlines defense and mitigation strategies. The post Turning Up the

The post-quantum future of web privacy
Cryptographic protocols like Privacy Pass help keep web sites safe from abuse while keeping their users private. This post looks at
Virtualization security: attack layers and misconfiguration impact
A detailed breakdown of misconfigurations in virtual environment cybersecurity as shown by examples of ransomware cases on ESXi and Proxmox

Cyberattacks: ‘I could see all my files on my computer going one by one’
Our CEO Brian Honan spoke to The Irish Times for a feature on the growing cyber threat facing Irish businesses.
Russian involvement in European attacks assessed as ‘credible’, security sources say
Our CEO Brian Honan spoke to the Irish Examiner about the wave of hybrid attacks that hit Europe this week.
Guiding Customers Through Critical PHP Vulnerabilities
Over the past week, our industry has faced a wave of critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619). As Palo
New Cortex XDR Integration with Claude Cowork Secures Desktop AI Agents
AI agents working directly on the desktop offer new ways to automate complex tasks, yet they operate outside traditional endpoint

The Internet’s New Factories
AI factories create several traffic systems at once, and power is shaping where they can be built. This article asks

Threat actors use agentic AI tooling to find and abuse exposed secrets
Microsoft Threat Intelligence has observed threat actors using the agentic offensive security framework ARTEX to search GitHub for OAuth application
How to navigate the SIEM correlation rule set | Kaspersky official blog
We’ve built a knowledge base for Kaspersky SIEM that makes working with correlation rules easier.Kaspersky official blogRead More
Malware Triage: Foundational Techniques to Separate Signal from Noise
6 steps, from fast static checks to escalation 4 possible outcomes: close, monitor, contain, or escalate 6 runtime behavior areas

What’s new in Microsoft Security: November 2026
Microsoft Security’s November 2026 updates strengthen AI agent security, least privilege, threat protection, and exposure management. The post What’s new
New investments to reduce on-premises security risk
We’re announcing a new on-premises security initiative, bringing together guidance, migration, and product investments. The post New investments to reduce

Email threat landscape: Q3 2026 trends and insights
Microsoft Threat Intelligence observed a sharp rise in email-based phishing activity at the end of Q3 2026 (July – September),

Agents aren’t humans (but they kinda are)
AI agents act for millions, but servers see intermediaries that strip user visibility. This post defines the problem space and
Latest

Google Pics: How to level up your visuals in Docs and Slides
Simplicity and convenience are a tough combo to beat. That’s why basic features integrated into the productivity apps we’re already
Google Pics: How to level up your visuals in Docs and Slides
Simplicity and convenience are a tough combo to beat. That’s why basic features integrated into the productivity apps we’re already

The Fridge-Hacking Spree Is an Internet-of-Things Wake-Up Call
Escalating hacks affecting blood labs and grocery stores show the very real risks to critical infrastructure that come from basic

Why a new report on Anthropic automating AI development is alarming researchers
Anthropic is using AI to build more powerful AI. And it appears to be working remarkably well, with the company’s

Trump’s hubris more comedy than tragedy but echoes Greek original
Recently across the globe, political observers have likened the foibles and subsequent downfalls of presidents of the United States to
CVE-2026-119508 | Mamunur Rashid Radius Booking Plugin up to 1.0.20 on WordPress authorization
A vulnerability marked as problematic has been reported in Mamunur Rashid Radius Booking Plugin up to 1.0.20 on WordPress. Affected
Wordfence Intelligence Weekly WordPress Vulnerability Report (October 26, 2026 to November 1, 2026)
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were
Hacking on Autopilot: Inside ARTEX Cybercrime Campaigns
Key Points Introduction ARTEX is a Chinese open-source, AI-powered penetration testing platform designed to help security teams assess systems they
Attackers Actively Probing for Upgrade-Window RCE Vulnerability in WordPress Core
On October 28th, 2026, the WordPress Security Team released WordPress 7.1.4, along with backported security releases for older branches, addressing
Why Higher Ed Needs a New Playbook for Ransomware, AI Risk, and Compliance
Discover how higher education institutions use Zero Trust microsegmentation and AI governance to contain ransomware and meet FERPA compliance.BlogRead More
ChatGPT Lockdown Mode Bypass: Phishing, Malware Delivery, and Silent Data Exfiltration
Research by: Alexey Bukhteyev Key Takeaways Introduction Earlier this year, Check Point Research disclosed a security flaw in ChatGPT’s code-execution
Your Threat Intelligence Stack Has Blind Spots. Here’s How to Close Them
Your SOC pays for multiple threat intelligence feeds, yet fresh malicious domains and IPs can still appear in telemetry as

The SOC Files 5: Ghost in the pipeline, or a fileless SharePoint breach by Storm-2603
Kaspersky researchers analyze a complex fileless cyberattack by Storm-2603 involving ToolShell exploitation and subsequent runtime subversion, and discuss how to

Do Registrars Use DNSSEC on Their Own Domains?
Registrars must support DNSSEC for customers, but how many use it themselves? A study of 698 registrar domains finds fewer
Talking hybrid-cloud infrastructure, IT modernization, and AI readiness with Michael Dickman and Shawn Lund
Cisco’s Michael Dickman and Deloitte’s Shawn Lund join AB to unpack the network, security, and governance shifts needed to scale
Synthetic CISOs Call AI Agents the Most Underestimated Risk
Synthetic CISOs rank AI agents as the top underestimated threat. See key survey findings and learn how to secure overpermissioned

See the agents, set the terms: new visibility and control for personal agents
Personal AI agents have changed how users interact with the web, blurring the lines between automated and human traffic. Learn
Detection Engineering: Implementing Detection-as-Code in an Existing Environment: Part 2 – Execution
Moving to Detection-as-Code starts with making existing detection data reliable and machine-readable. In Part 2, we explain how we validated
The RIPE Chair Team Reports – Highlights from RIPE 93
From digital independence and practical AI to inclusion and research, RIPE 93 gave the community plenty to discuss and act
How Cisco defends at machine speed with OpenAI
Cisco combines network intelligence and OpenAI models to build more adaptive defenses.More RSS Feeds: https://newsroom.cisco.com/c/r/newsroom/en/us/rss-feeds.htmlCisco Newsroom: SecurityRead More

Microsoft named a Leader in the 2026 Gartner® Magic Quadrant™ for AI Agent Management Platforms
Read why Gartner named Microsoft a Leader in the inaugural 2026 Magic Quadrant for AI Agent Management Platforms. The post

Fake-download campaign uses trojanized installers to deliver monetization payloads
Microsoft Threat Intelligence tracks a fake-download campaign that uses trojanized Inno installers to deliver multiple monetization offers and provides detection
Wordfence Price Increase Coming December 3, 2026
On Thursday, December 3, 2026, pricing for Wordfence Premium, Care, and Response will increase. We’re announcing this change a month
Akamai Named a Leader in 2026 IDC MarketScape for Managed Edge
IDC MarketScape named Akamai a Leader in Managed Edge Services 2026. Discover how edge computing drives low-latency, secure AI inference

Introducing Zero Wire, a hub for investigating critical Internet vulnerabilities
Zero Wire on Cloudflare Radar pairs plain-language briefings with global attack telemetry and remediation steps. Triage critical CVEs faster and
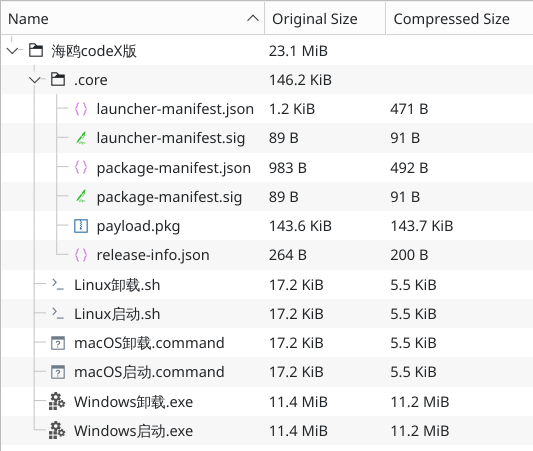
Free the Model, Sell the Gateway: Prompt Adware hidden in Jailbreak Bundles
Key Points Free the Model, Sell the Gateway: Prompt Adware hidden in Jailbreak Bundles Check Point Research found a misconfigured
PHP2Shell: what we know about the threat two weeks later | Kaspersky official blog
Nearly 30 million servers still haven’t been updated. Who’s attacking and how, why you need to install the second round
Major Cyber Attacks in October 2026: Fake AI, Account Takeovers, and Remote Access Threaten US and EU
October 2026 brought another wave of cyber threats targeting US enterprises, exposing security gaps that could lead to financial losses,
MLEP in KICS for Networks 5.0: how machine learning helps track network behavior of OT devices
We explain how Kaspersky Industrial CyberSecurity for Networks uses Machine Learning Event Processor (MLEP) technology to help take inventory of
How do you hack a supermarket fridge, and why would anyone want to?
Speaking to The Journal, our CEO, Brian Honan, explains how connected refrigeration systems allow suppliers to monitor equipment and detect
Release Notes: Related Threat Context for Faster Than Ever SOC Triage and 590+ Coverage Updates
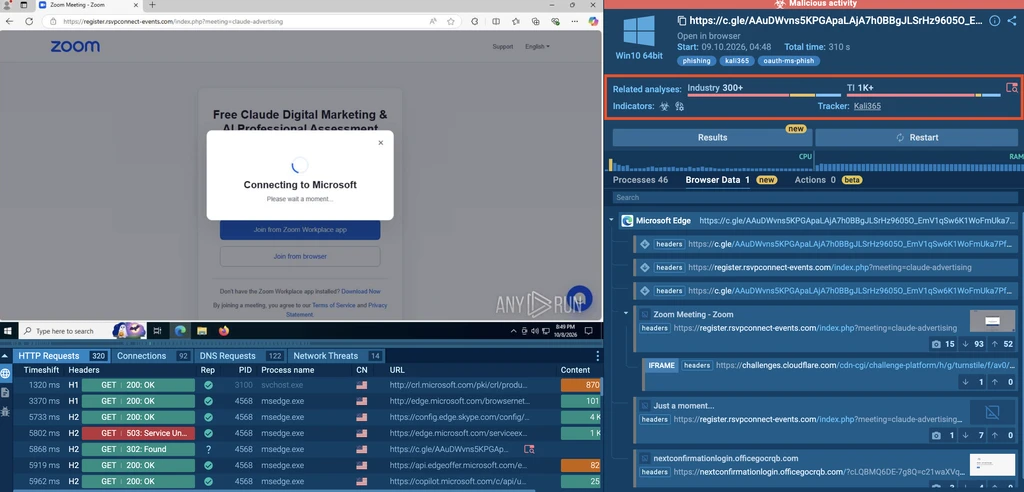
Security investigations often begin with a single suspicious IOC, but deciding what it means requires context. The more relevant intelligence

SuperValu says all stores back to normal as EU retailers count costs of cyber attacks
Our CEO, Brian Honan, spoke to the Irish Independent about the risks associated with internet connected equipment. The disruption is
Unit 42 Threat Intelligence Highlights – Nov. 2, 2026
Unit 42 details recent threat intelligence, highlighting cyberespionage, financial extortion, and the rapid adoption of AI across offensive workflows. The
How Skyfire and Akamai Enabled 2.5 Million Agentic Transactions
Discover how Akamai and Skyfire verify AI shopping agents with Know Your Agent (KYA) to securely enable agentic commerce and
CVE-2026-98432: A Remote Use-After-Free in the Linux Kernel’s TCP Stack
Learn about CVE-2026-98432, a critical remote use-after-free flaw in the Linux kernel TCP stack, its root exploit risks, affected versions,
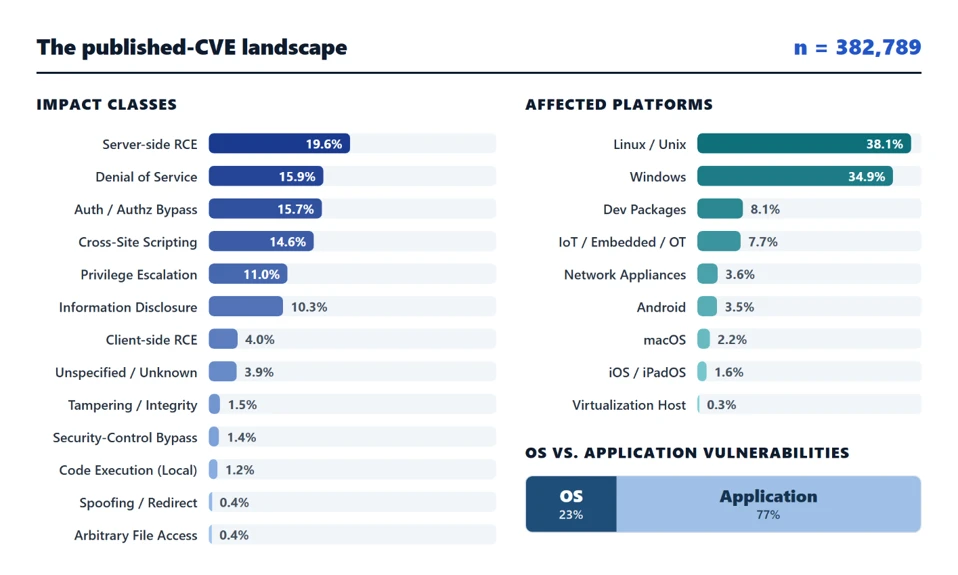
What exploited vulnerabilities have in common: A data-driven analysis of real-world attacks
Real-world exploitation concentrates in a small, high-impact subset of CVEs. Learn how defenders can prioritize vulnerabilities based on exploitation likelihood,
2nd November – Threat Intelligence Report
For the latest discoveries in cyber research for the week of 2nd November, please download our Threat Intelligence Bulletin. TOP
HTTP2Shell: What the Critical Brotli Vulnerability Means for WordPress Sites
On October 22, 2026, Google published CVE-2026-111497, a critical vulnerability in Brotli, one day after the Brotli project released fixed
How a surveillance camera can be remotely disabled: the problem and the fix | Kaspersky official blog
A vulnerability in Intelbras cameras allows them to be remotely disabled. We explain the issue, and how to fix it.Kaspersky

How we halved DNS build delay and cut memory use by 85%
Zone setting changes used to rebuild entire DNS zones, even ones with tens of millions of records. Here is how
it-sa 2026 Recap: Key Trends Shaping Security Operations
From October 27 to 29, the ANY.RUN team joined it-sa 2026 in Nuremberg, meeting customers, partners, SOC and MSSP teams,

CyberStrikeAI in the wild: the use of AI in real-world attacks on organizations
We analyze a series of attacks on educational institutions that were fully automated during the post-exploitation phase using the CyberStrikeAI
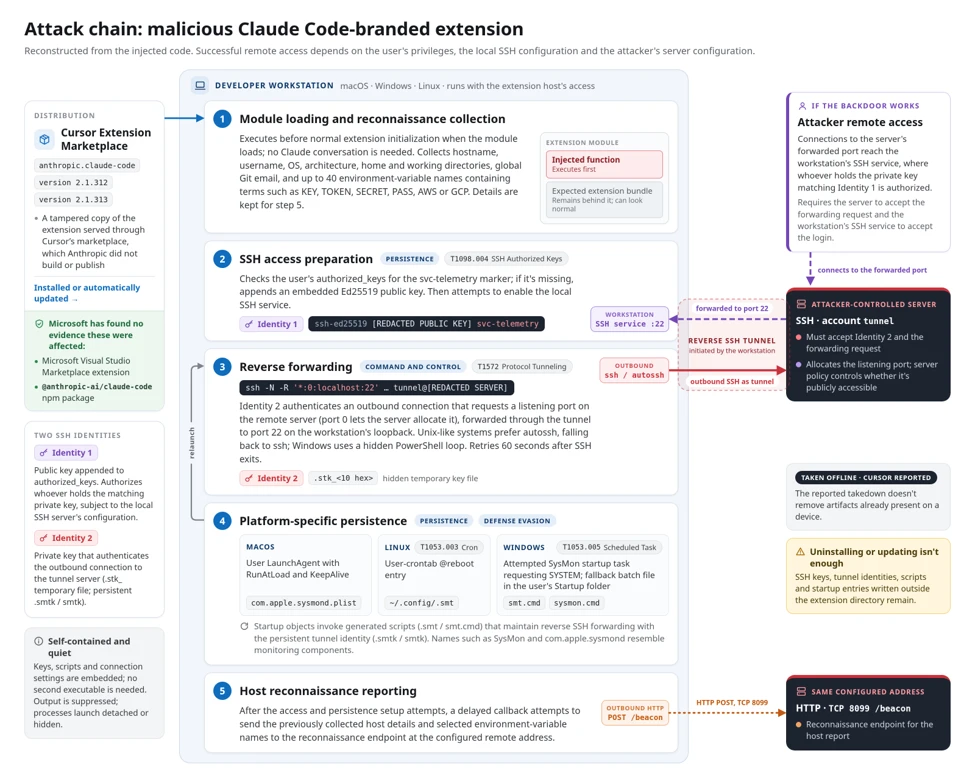
Inside a malicious Claude Code-branded extension and its persistent SSH backdoor
Microsoft analyzes a malicious Claude Code–branded extension, its persistent SSH backdoor, and guidance to detect and remediate it. The post
Detection Engineering: Implementing Detection-as-Code in an Existing Environment: Part 1 – Introduction and Concept
How do you introduce Detection-as-Code into an environment where detections are already being developed and deployed? This customer case study
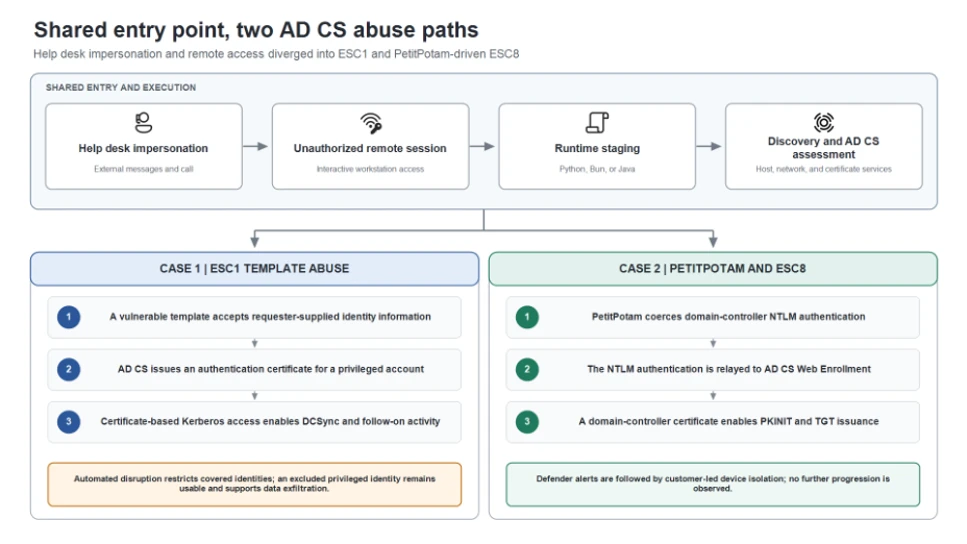
From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths
Teams support impersonation led to remote access, malicious runtime execution, and Certificate Services abuse through authentication relay and Kerberos. The

4 real? Tracking exploitation and patching of eMudhra’s weak keys
Four, just four: that’s the key to break into any unpatched connection on the Internet that is using eMudhra certificates. Here’s
How to download and read ebooks safely | Kaspersky official blog
We explain how to download and read ebooks safely, whether a device can be infected through an ebook, and why

Cloudflare services for private origins is now generally available
Public traffic to private origins, with WAF, bot management, caching, and Workers, is now available to every customer with Cloudflare
There’s a Security Deal Hiding in Your Customer’s Browser
Discover how the Akamai Workforce Protector Partner Playbook helps you secure browser AI interactions, eliminate data visibility gaps, and close
Filter generation in practice: from algorithms to LLMs
We automate filter generation for security alerts using an algorithm, a large language model, and a group of LLM agents.SecurelistRead
WordPress 7.1.4 Patches Unauthenticated Upgrade-Window RCE; Exploitation Attempts Detected After Release
TL;DR: WordPress 7.1.4 was released on October 28, 2026. According to WordPress, it includes fixes for 22 security vulnerabilities. The
Wordfence Bug Bounty Program Monthly Report – July 2026
In July 2026, the Wordfence Bug Bounty Program received 1077 vulnerability submissions from our growing community of security researchers working

IDC MarketScape names Microsoft a Leader in the 2026 Worldwide Modern Endpoint Security for Enterprises Vendor Assessment
IDC has named Microsoft a Leader in the 2026 IDC MarketScape for Worldwide Modern Endpoint Security for Enterprises. The post

Tracking AI adoption in North Korean threat actor tradecraft
As Microsoft Threat Intelligence continues to track how threat actors operationalize AI to increase the speed and efficiency of attacks,
Akamai Cloud Is Scaling for What Comes Next (Updated October 2026)
Explore Akamai Cloud’s Q3 2026 updates: expanded NVIDIA RTX PRO™ 6000 GPUs, Valkey Managed Database, LKE Enterprise Kubernetes scaling, and
Wordfence Intelligence Weekly WordPress Vulnerability Report (October 19, 2026 to October 25, 2026)
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were
‘Critical Vulnerabilities’ Found in Computer Code Supporting 70% of the Internet
Critical vulnerabilities in PHP, the code behind up to 70% of the internet, have forced websites across Europe offline as

Cohere’s Qwen Story: Looks More Like Model Jaggedness
Key findings On October 26, Cohere reported a puzzling incident involving Qwen3.8-Flash-Next, an open-weight model from Alibaba. The task was
Applying Security by Design and Cyber Immunity principles to protect AI systems | Kaspersky official blog
How organizations can use the basic principles of secure system design to reduce the risks of deploying AI agents: a

Cloudflare DDoS Threat Report 2026 Q3: More swarms, fewer giants
Add your teaser here. It should complement the headline, not repeat it. Teaser cannot be longer than 240 characters. The Blog Review Gem will
Security Roundup October 2026
Curated advice, guidance, learning and trends in cybersecurity and privacy, as chosen by our consultants. Experienced security advice on demand

Beyond Framework Signatures: Understanding AI-Driven Intrusions
The post Beyond Framework Signatures: Understanding AI-Driven Intrusions appeared first on Nextron Systems.Nextron SystemsRead More
Unknown APT uses NetamLoader to attack a Win10 OS customized for governments in Asia
Kaspersky researchers analyze a complex targeted attack employing NetamLoader, a sophisticated malicious framework and targeting a customized government OS.SecurelistRead More
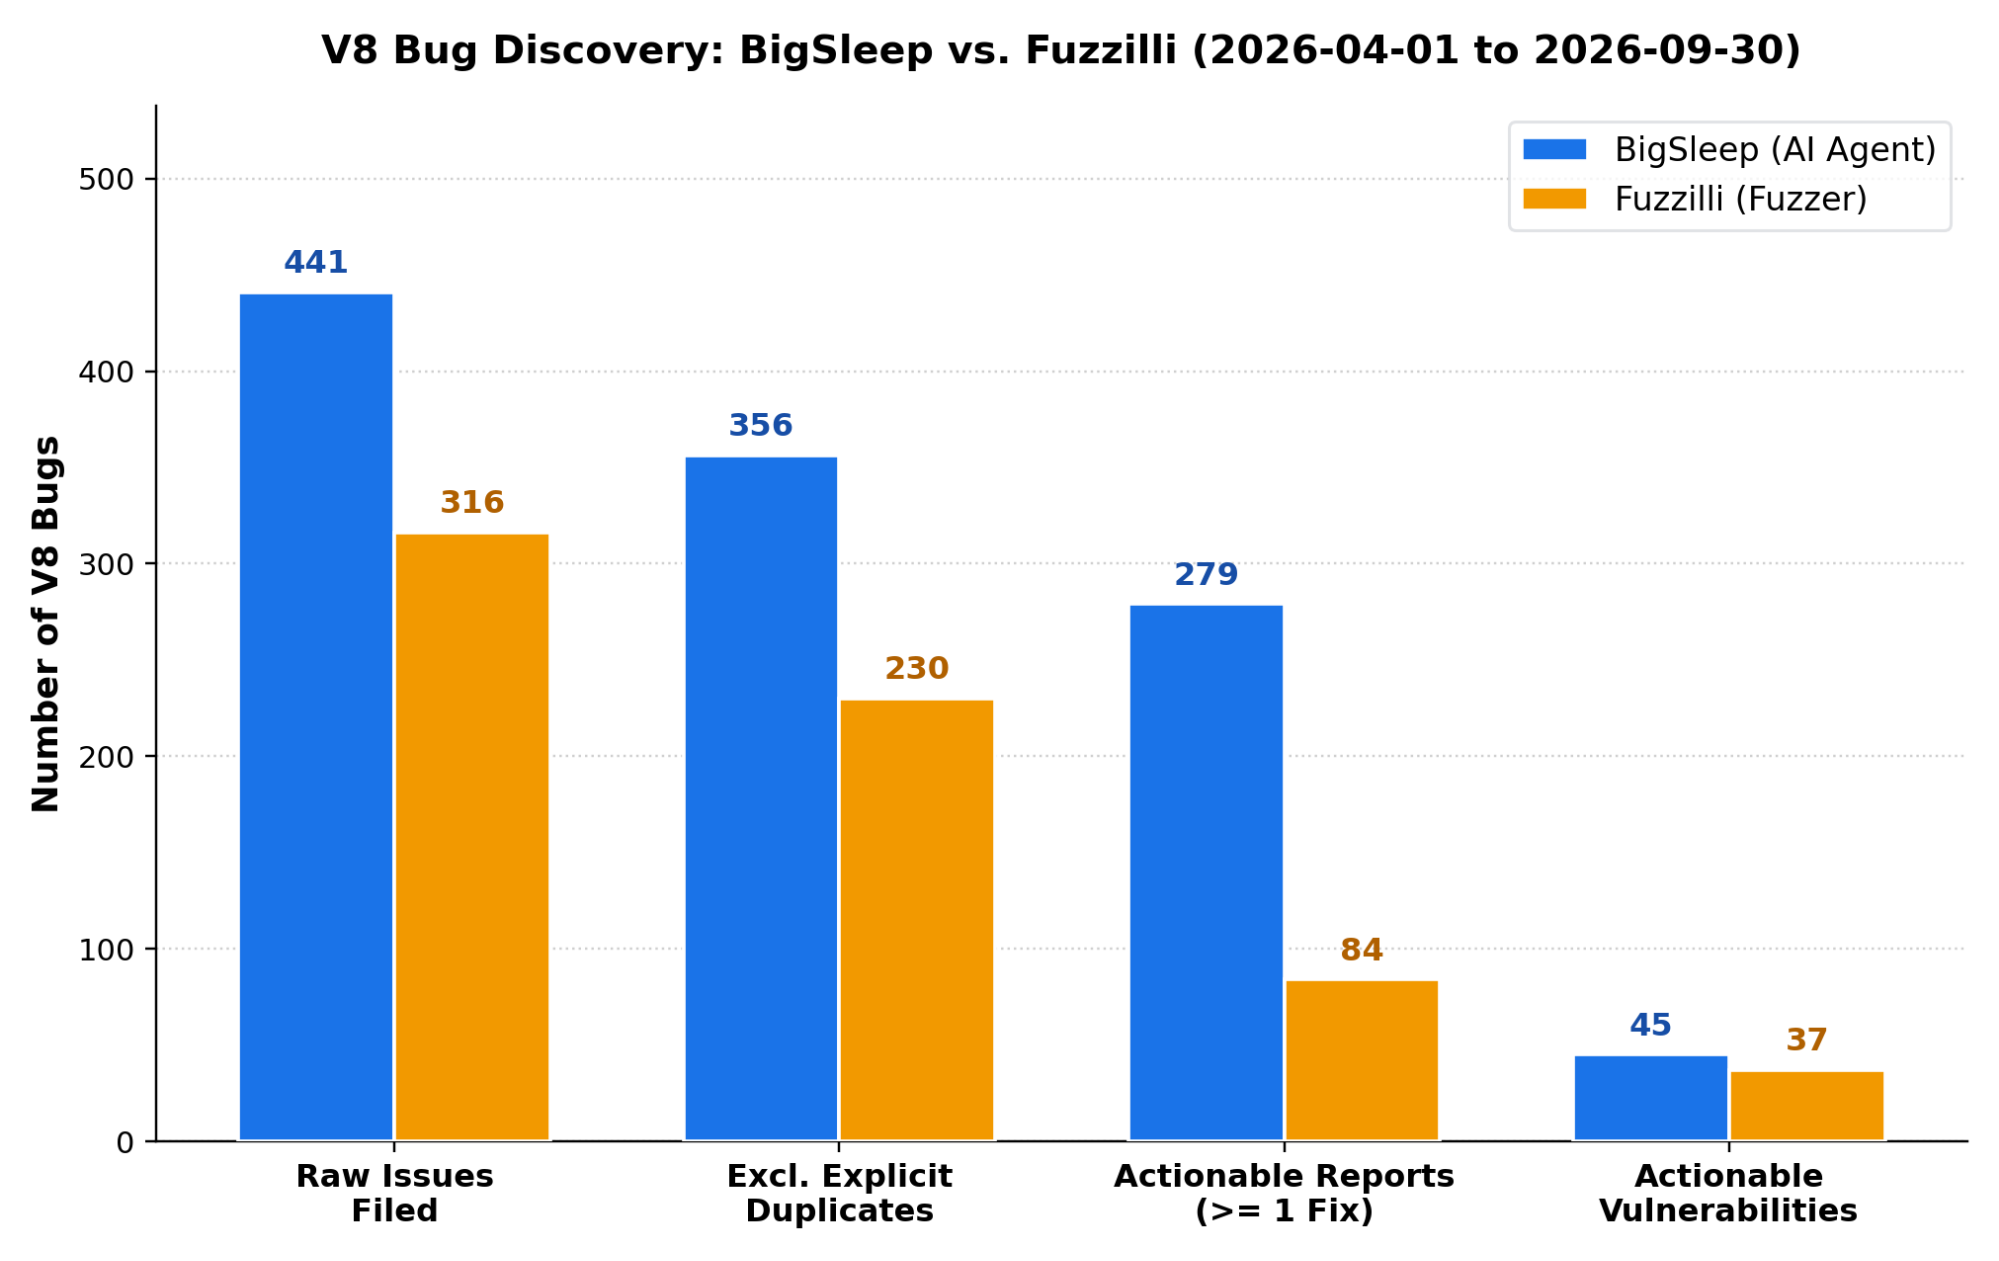
Fuzzers vs. AI: Comparing Fuzzilli and BigSleep on JavaScript Engines
Summary Project Zero compared two automated tools used by Google to find vulnerabilities in Chrome’s JavaScript engine, V8, on a
PHP2Shell Update: Still No Confirmed WordPress Compromises, and Answers to the Questions We’re Hearing Most
As of October 28, 2026, Wordfence knows of no WordPress site compromised through PHP2Shell. Update PHP to a fixed version

The CISO’s evolving role: Protecting and defending in the agentic era
As AI and agents reshape the enterprise, CISOs face two critical priorities: enabling innovation with the right identity and data

Unwrapping Retail Peak Season Cyber Threats
Unit 42 explores key peak shopping season retail cyber threats, from ransomware to AI attacks, and shares how to defend
How the ClickFix tactic exploits trust, and what you can do about it
Social engineering appeals to people’s better nature, and cybercriminals know this. That’s why it’s still one of the most widely
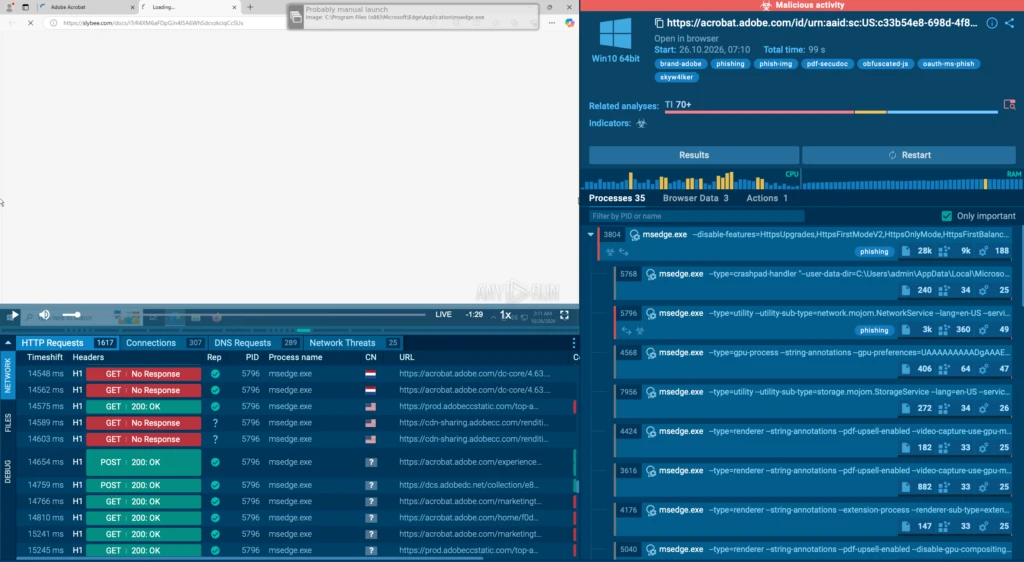
AI-Powered Malware & Phishing Analysis for SOC Teams: Cut Workload and Speed Up Response
AI is now everywhere in cybersecurity. But how much of it is actually making SOC teams’ jobs easier? Almost every
Millions of security cameras at risk: DoS vulnerability in Intelbras devices
During our research, we discovered a denial-of-service vulnerability that could affect millions of Intelbras IP camera systems built on the
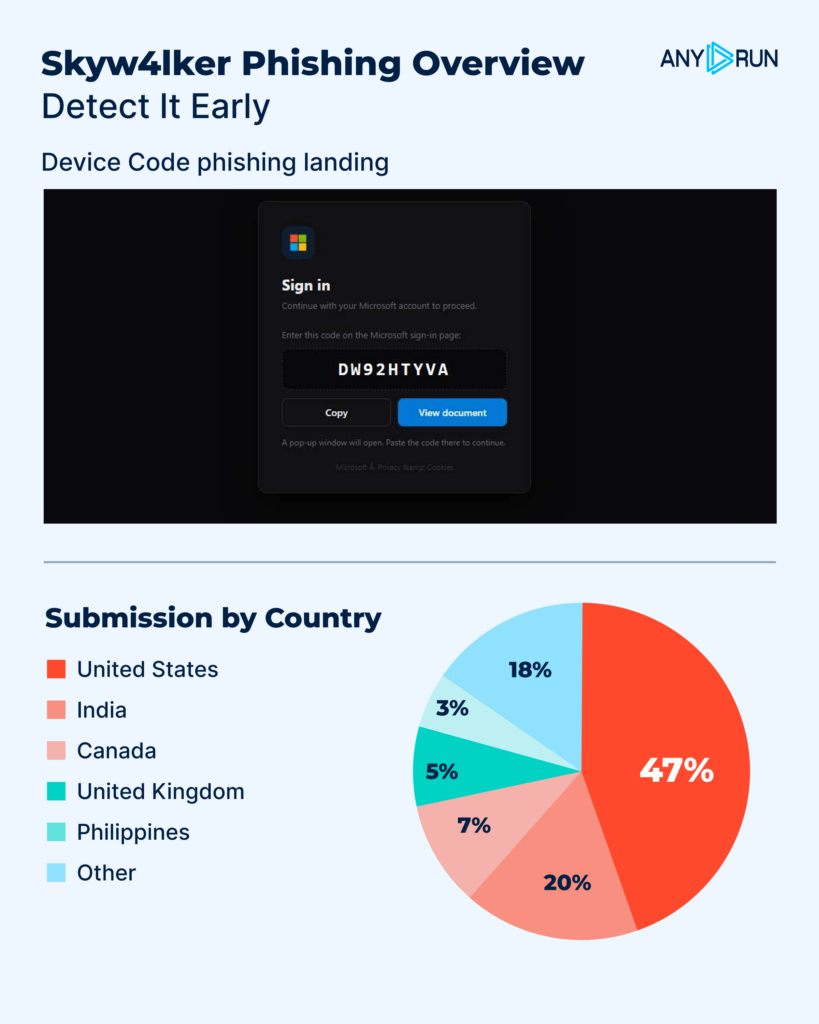
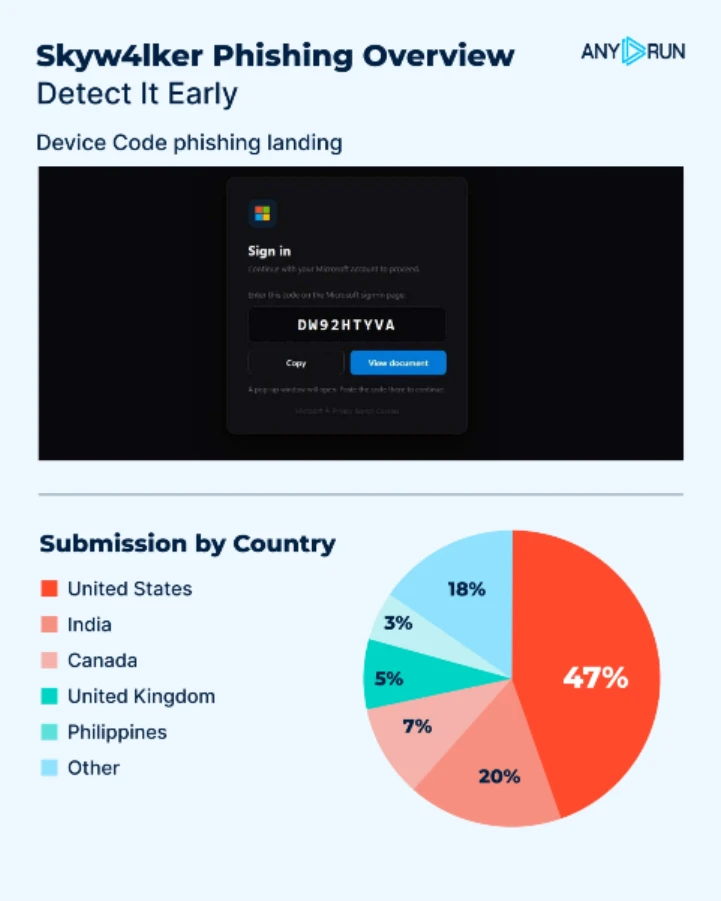
SkyW4lker Exposed: A Growing Microsoft 365 Phishing Threat to American Enterprises
SkyW4lker (SkyW4lker x365 Sentinel) is an active device-code phishing kit targeting Microsoft 365 users in the United States, Europe, and

What took the Internet offline in Q3 2026
An examination of global Internet disruptions observed by Cloudflare Radar during the third quarter of 2026. This review analyzes how

Introducing the Cloudflare PHP Capture the Flag challenge
We are launching a PHP Capture the Flag challenge integrated with our Bug Bounty program to test our WAF protections.

Tricks from the Past deployed via signed ChatGPT and Claude binaries
Key Points Introduction Over the past two months, we have been tracking a campaign that abuses the popularity of AI
SARS tax refund phishing: tracing a global phishing kit
Threat researchFollowing the refund: how fake South African government sites led to a global phishing kitTwo phishing domains from VMRay
An insecure neighbor: how a vulnerability chain led to an isolation bypass in cloud infrastructure
A Kaspersky expert presents a cloud isolation bypass case honored at Russian Pentest Award 2026. Learn how vulnerabilities in Kubernetes,
SIDN Publishes RSSAC002 Traffic Metrics for .nl
SIDN Labs has released open DNS traffic data for .nl in the same format used by root server operators. In

Cross-request KV cache exposure in the GLM-5.3 Workers AI model, and our remediation with SGLang
A configuration mismatch in GLM 5.3 on Workers AI triggered an SGLang bug that exposed KV cache pages across requests.
RIPE 93 Daily Meeting Blog
RIPE 93 has kicked off in wonderful ancient Sofia. As always, you can view the slides, you can watch the

Security Center 3.0: Multi-Tenancy, Advanced Access Control and User API
The post Security Center 3.0: Multi-Tenancy, Advanced Access Control and User API appeared first on Nextron Systems.Nextron SystemsRead More

Management Center 4.3: A New Interface and Smarter THOR Exclusions
The post Management Center 4.3: A New Interface and Smarter THOR Exclusions appeared first on Nextron Systems.Nextron SystemsRead More

Analysis Cockpit 4.5: More Efficient Case Management and Improved Operations
The post Analysis Cockpit 4.5: More Efficient Case Management and Improved Operations appeared first on Nextron Systems.Nextron SystemsRead More
26th October – Threat Intelligence Report
For the latest discoveries in cyber research for the week of 26th October, please download our Threat Intelligence Bulletin. TOP
Introducing the Wordfence Threat Response Team: A New Way to Report Active Threats in the WordPress Ecosystem
The Wordfence Threat Response Team is a new small, technically hands-on team responsible for turning rapidly emerging threats into customer
Cybersecurity in Christopher Nolan’s The Odyssey | Kaspersky official blog
What Christopher Nolan’s The Odyssey can teach us about cybersecurity, and what risks watching the movie entailsKaspersky official blogRead More

Deploying AI agents securely: how Kaspersky products mitigate AI threats
We look at best practices for deploying AI tools securely in corporate environments, with Kaspersky Security Center and Kaspersky Endpoint
Wordfence Intelligence Weekly WordPress Vulnerability Report (October 12, 2026 to October 18, 2026)
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were
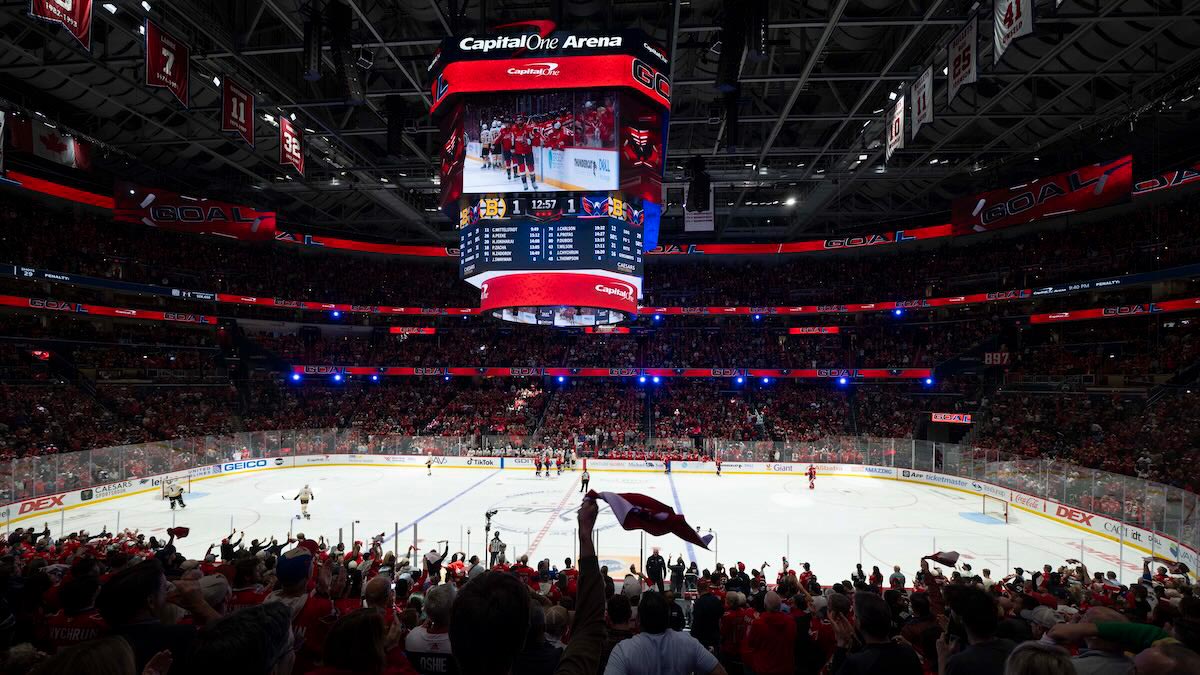
At Capital One Arena, a winning goal for the network
Behind the scenes at a Washington Capitals game, a Cisco partnership ensures a dazzling fan experience.More RSS Feeds: https://newsroom.cisco.com/c/r/newsroom/en/us/rss-feeds.htmlCisco Newsroom:

Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks
Microsoft Threat Intelligence analyzes the LiteLLM 1.107.0 compromise, including Python startup hooks, credential theft, remote code loading, detections, and mitigations.

Bringing post-quantum cryptography to geographically fenced key management
Cloudflare’s new post-quantum GeoKey Manager protects geographically fenced decryption keys from harvest now, decrypt later attacks. Learn how we redesigned

Origin Range Requests: Serving large files without range-request tuning
Naive byte-range caching can waste gigabytes of origin bandwidth on small requests. We rebuilt our cache architecture in Pingora to
Technology that blocks DGA domains | Kaspersky official blog
Kaspersky email security solutions now include a technology that detects domains with auto-generated names.Kaspersky official blogRead More
PHP2Shell Operational Guidance
This public operational guidance for PHP2Shell is provided to customers and published for the benefit of the wider community.NVISO LabsRead

Infostealer riding the AI Train
Key Points Introduction Infostealers commonly target browser passwords, session cookies, and cryptocurrency wallets. This malware combines those established capabilities with

CAPIF 5 Meeting Report: More Local Routes, Stronger Regional Connections
More local peering, stronger routing security and a shared ambition to improve connectivity: CAPIF 5 brought Central Asia’s Internet community
Beyond Day Zero: Akamai’s Rapid Response and AI Threat Intelligence
Discover how Akamai responded to critical PHP vulnerabilities using agentic AI, real-time telemetry, and rapid action switching to deliver adaptive
Attacks on PHP2Shell Continue, But No Known Compromises as a Result Yet
On October 21st, 2026, the PHP project released emergency updates for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619. We
How new PHP vulnerabilities threaten home users | Kaspersky official blog
Two critical PHP vulnerabilities (CVE-2026-109618 and CVE-2026-109619) pose a risk to home users and their data. We explain the danger