Incorrect Authorization vulnerability (CVE-2026-106030) has been found in NordVPN software.CERT PolskaRead More
CERT announcements

Podatność w oprogramowaniu NordVPN
W oprogramowaniu NordVPN wykryto podatność typu Incorrect Authorization (CVE-2026-106030).CERT PolskaRead More
Komunikacja kryzysowa w cyberbezpieczeństwie
Cisza po incydencie cyberbezpieczeństwa jest równie groźna jak sam atak. Gdy brakuje rzetelnych informacji, szybko pojawiają się plotki, domysły i
Podatność w oprogramowaniu Sparx Systems Enterprise Architect
W oprogramowaniu Sparx Systems Enterprise Architect wykryto podatność typu Improper restriction of XML external entity reference (CVE-2026-88794).CERT PolskaRead More
Latest

6 wild ways to make Android widgets more useful
Widgets, widgets, widgets. Has there ever been an Android feature so full of promise that went unloved by Google for

Vulnerability in Sparx Systems Enterprise Architect software
Improper restriction of XML external entity reference vulnerability (CVE-2026-88794) has been found in Sparx Systems Enterprise Architect software.CERT PolskaRead More
Podatności w centralach telefonicznych Slican
W centralach telefonicznych Slican wykryto 3 podatności różnego typu (CVE-2026-35088, CVE-2026-63314 oraz CVE-2026-63315)CERT PolskaRead More
Vulnerabilities in Slican telephone exchanges
CERT Polska has received a report about 3 vulnerabilities (CVE-2026-35088, CVE-2026-63314 and CVE-2026-63315) found in Slican telephone exchanges.CERT PolskaRead More

Using TLS to protect data
Recommended profiles to securely configure TLS for the most common versions and scenarios, with additional guidance for managing older versions.All
Post-quantum updates to our TLS guidance
The NCSC publishes its recommendations for configuring post-quantum cryptography in TLS. Now is time to migrate.All FeedRead More
TR-101 Security Recommendations for Industrial, Operational Technology (OT) and Internet of Things (IoT) Devices
TR-101 – Security Recommendations for Industrial, Operational Technology (OT) and Internet of Things (IoT) Devices Overview Industrial, Operational Technology (OT)

A Five-Step Framework to Sufficient Realism in Cyber Simulations
This blog post proposes a five-step framework for determining the needed realism of a simulated environment.SEI BlogRead More
Vulnerability in Payload CMS software
SQL Injection vulnerability (CVE-2026-63316) has been found in Payload CMS software.CERT PolskaRead More
Podatność w oprogramowaniu Payload CMS
W oprogramowaniu Payload CMS wykryto podatność typu SQL Injection (CVE-2026-63316).CERT PolskaRead More
Help the NCSC understand how organisations approach external attack surface risk
We’re looking to hear from people involved in evaluating, selecting or adopting EASM.All FeedRead More

China-linked malicious actors called out by UK and international partners for targeting sensitive data globally
Joint advisory with international partners highlights malicious targeting of organisations from a range of sectors across the globe.All FeedRead More
Vulnerability in Ollama software
Relative Path Traversal vulnerability (CVE-2026-103663) has been found in Ollama software.CERT PolskaRead More
Podatność w oprogramowaniu Ollama
W oprogramowaniu Ollama wykryto podatność typu Relative Path Traversal (CVE-2026-103663).CERT PolskaRead More

Incident affecting ASOS customers
ASOS has said it is investigating a cyber incident and that some customer personal information may have been accessed.All FeedRead

Navigating Program Complexity with the Waypoints Framework
Learn how the Waypoints Framework helps program managers visualize activities, synchronize dependencies, and manage risks effectively.SEI BlogRead More
Podatności w oprogramowaniu GNU Aspell
W oprogramowaniu GNU Aspell wykryto 3 podatności różnego typu (od CVE-2026-75818 do CVE-2026-75820)CERT PolskaRead More
Vulnerabilities in GNU Aspell software
CERT Polska has received a report about 3 vulnerabilities (from CVE-2026-75818 to CVE-2026-75820) found in GNU Aspell software.CERT PolskaRead More
Operational Guidance for Incident Handling – Rulebooks
Operational guidance for incident handling Traffic Light Protocol (TLP): CLEAR Version: 1.0 (stable) Date: 28 September 2026 Authors: Agence Nationale
Publications and Presentations
Publications Description Last update TR-100 – Multiple Critical Vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway 27th September 2026 TR-99
Podatność w oprogramowaniu Ghostscript
W oprogramowaniu Ghostscript wykryto podatność typu Untrusted Search Path (CVE-2026-19547).CERT PolskaRead More
Podatność w oprogramowaniu MyPresta Google Merchant Center Feed
W oprogramowaniu MyPresta Google Merchant Center Feed wykryto podatność typu External control of file name or path (CVE-2026-85520).CERT PolskaRead More
Vulnerability in MyPresta Google Merchant Center Feed software
External control of file name or path vulnerability (CVE-2026-85520) has been found in MyPresta Google Merchant Center Feed software.CERT PolskaRead
Podatność w oprogramowaniu Quick.Cart
W oprogramowaniu Quick.Cart wykryto podatność typu Cross-Site Request Forgery (CSRF) (CVE-2026-41875).CERT PolskaRead More
Vulnerability in Quick.Cart software
Cross-Site Request Forgery (CSRF) vulnerability (CVE-2026-41875) has been found in Quick.Cart software.CERT PolskaRead More
Choosing the Hardware That Will Put DARPA MOCHA’s Compilers to the Test
How do you select the best hardware to test next-gen compilers? Our latest post explores how the SEI is tackling
Vulnerabilities in YunoHost-Apps sogo_yhn software
CERT Polska has received a report about 2 vulnerabilities (CVE-2026-74864 and CVE-2026-74865) found in YunoHost-Apps sogo_yhn software.CERT PolskaRead More
Podatności w oprogramowaniu YunoHost-Apps sogo_yhn
W oprogramowaniu YunoHost-Apps sogo_yhn wykryto 2 podatności umożliwiające obejście uwierzytelnienia (CVE-2026-74864 oraz CVE-2026-74865)CERT PolskaRead More
Vulnerability in gotop software
Local Argument Injection vulnerability (CVE-2026-91784) has been found in cjbassi/gotop software.CERT PolskaRead More
Podatność w oprogramowaniu gotop
W oprogramowaniu cjbassi/gotop wykryto podatność typu Local Argument Injection (CVE-2026-91784).CERT PolskaRead More
CERT-FR riasztás
A Midnight Blizzard, az Oroszország által támogatott fejlett tartós fenyegetés (APT), amely a 2016-os amerikai választásokba való beavatkozás és a
BSI: 17.000 Exchange szerver veszélyben Németországban
A Németországban található mintegy 45 000, az internetről korlátozás nélkül elérhető Microsoft Exchange-kiszolgáló mintegy 12%-a annyira elavult, hogy a gyártó
EU Katonai Törzs: Az uniós országoknak szorosabb együttműködésre van szükségük a kiberbiztonság terén
A Nemzetközi Biztonságpolitikai Konzultatív Fórumon egy szakértői panel hangsúlyozta a kibertámadások növekvő fenyegetését, valamint a katonai, állami és magánipari együttműködés
Erőltetett kiberbiztonság?
Az Európai Unió (EU) tovább halad előre a kiberbiztonságról szóló törvényjavaslat, a Cyber Resilience Act (Kiberbiztonságról szóló törvény) ügyében, amely
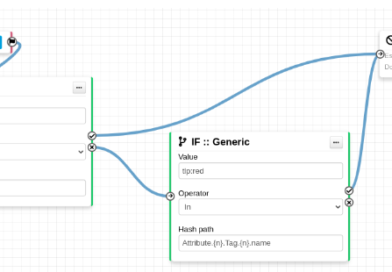
Számos új fukcióval bővült a MISP
A MISP (Malware Information Sharing Platform) új korrelációs motorral, új munkafolyamatokkal bővült a mostani kiadásában. FORRÁS
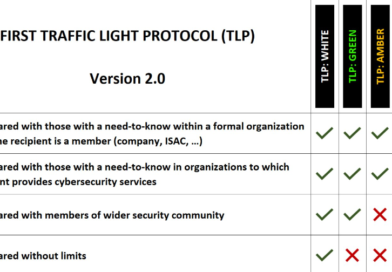
Az új közlekedési lámpa protokol (2.0) megjelent
Augusztól alkalmazandó az új Traffic Light Protocol (TLP), melyben FIRST meghatározza/pontosítja a jelölések formai követelményeit és tartalmát. FORRÁS
Signal biztonsági beállítások
CERT-EU kiadott egy útmutatót a Signal biztonsági beállítások módosítására az alábbi javaslatokkal. Minden esetben a hivatalos oldalt használja a Signal

Windows 10 hardening ajánlások
A német BSI támogatásával és szakmai felügyeletével az ERNW GmbH, egy független IT biztonsági szolgáltató közreműködésében adta ki legújabb, Windows 10 hardening témájú ajánlását.
A szlovák CERT egy régiót érintő, jelentős mértékű kibertámadásra figyelmeztet
Április 16-án pénteken a szlovák CERT (SK-CERT, NBÚ) rendkívüli figyelmeztetést adott ki, az országot és Közép-Európát érintő kibertámadással kapcsolatban. A figyelmeztetés nem tartalmaz részleteket, mindazonáltal leírják, hogy zsarolóvírus (ransomware) támadások várhatóak, illetve, hogy az állami, a telekommunikációs és az IT szektor leginkább veszélyeztetett.
Újabb kórház a zsarolóvírusok kereszttüzében
Január 17-én vasárnap zsarolóvírus támadás érte a belga CHwapi kórházat, ahol a támadás következtében beavatkozásokat kellett elhalasztani és betegeket kellett átirányítani más intézményekbe. Az intézmény jelentése szerint a támadás vasárnap este 20:45 perc körül érte a kórházat, és több, mint 80 eszköz még mindig titkosítva van. Az üzemeltető személyzet próbálkozásai az irányítás visszaszerzésére jelenleg hatástalanok. Az eset furcsasága, hogy a zsarolóvírusokra egyáltalán nem jellemző módon, a támadók egyelőre nem követeltek váltságdíjat, illetve adatlopás nyomait sem fedezték még fel a szakértők.