CSuite Targets US and EU Organizations with Device-Code Phishing and Remote Access
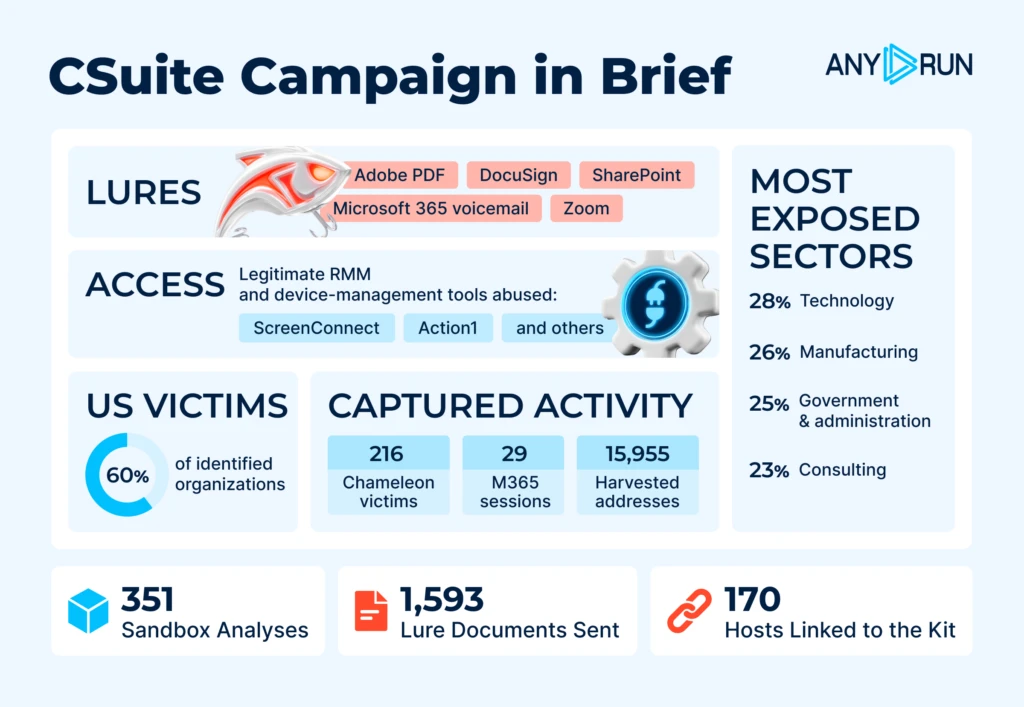
ANY.RUN researchers investigated CSuite, a phishing and remote-access operation that combines credential theft, Microsoft 365 session hijacking, and the abuse of legitimate management tools. The campaign showed a strong US focus, with 60% of identified victim organizations based in the United States. By blending trusted business services with legitimate remote-access software, CSuite can give attackers
The post CSuite Targets US and EU Organizations with Device-Code Phishing and Remote Access appeared first on ANY.RUN’s Cybersecurity Blog.ANY.RUN’s Cybersecurity BlogRead More