PSA: Critical Apache HTTP/2 Vulnerability: What WordPress Site Owners Should Know
Apache has released a fix for a critical vulnerability in the HTTP/2 module of Apache HTTP Server. The issue, CVE-2026-119618,
Read More
Apache has released a fix for a critical vulnerability in the HTTP/2 module of Apache HTTP Server. The issue, CVE-2026-119618,
Read More
Our analysis of how attackers used the open-source Cairn AI agent framework to autonomously breach semiconductor, defense and civic targets.
Read More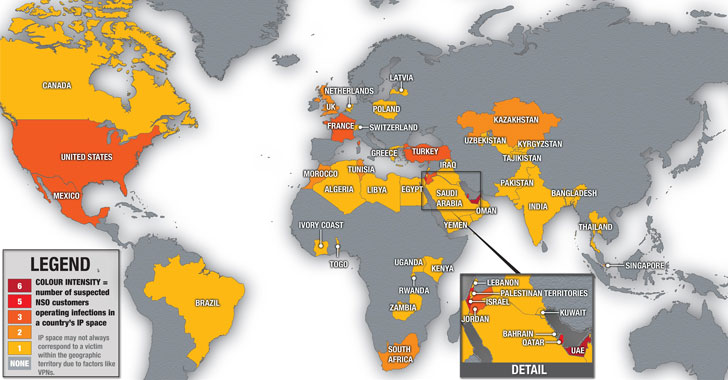
Europe’s spyware victims face years of legal battles and few answers as governments shield surveillance behind national security. Greek journalist
Read More
Upgrade, migrate, but don’t prevaricate – time has run outwww.theregister.com – ArticlesRead More
Read More
Endpoint management platforms can become powerful attack tools when compromised, allowing hackers to deploy malware, execute commands, and disrupt thousands
Read More
As governments adopt AI, workers are gaining ground in how it’s used and securing safeguards against its harmsIn the shadow
Read More
Europol and law enforcement partners from nine countries have seized hundreds of servers and domains used by the Gootloader, CastleRAT,
Read More
Amazon Prime subscribers can jump on a pretty nice deal happening on Ecoflow’s laptop power bank that can deliver up
Read More
Jensen Huang resigned as CEO of Nvidia this morning, a company he co-founded in 1993. The decision came following the
Read MoreA vulnerability, which was classified as critical, has been found in PostgreSQL up to 14.24/15.19/16.15/17.11/18.6. Impacted is the function ts_rank_cd.
Read More