CVE-2026-126815 | XauenDevs Lagarto Chivato up to 0.4.2/0.4.3 improper authentication
A vulnerability was found in XauenDevs Lagarto Chivato up to 0.4.2/0.4.3. It has been declared as critical. The affected element
Read MoreA vulnerability was found in XauenDevs Lagarto Chivato up to 0.4.2/0.4.3. It has been declared as critical. The affected element
Read MoreA vulnerability was found in Palo Alto Networks Checkov up to 3.4.1. It has been rated as critical. The impacted
Read MoreA vulnerability categorized as very critical has been discovered in OPSWAT MetaDefender Endpoint Security SDK up to 4.3.4821. This affects
Read More
Pixel users also get a bonus Wi-Fi upgrade. Here’s what to know.news – ZDNETRead More
Read More
The company had argued that the case, involving eight former workers, must be resolved before an arbitrator.NYT > TechnologyRead More
Read More
Missing trades, delayed quotes and wrong timestamps distort order-flow analysis. Learn how market data feed integrity affects charts and trading
Read More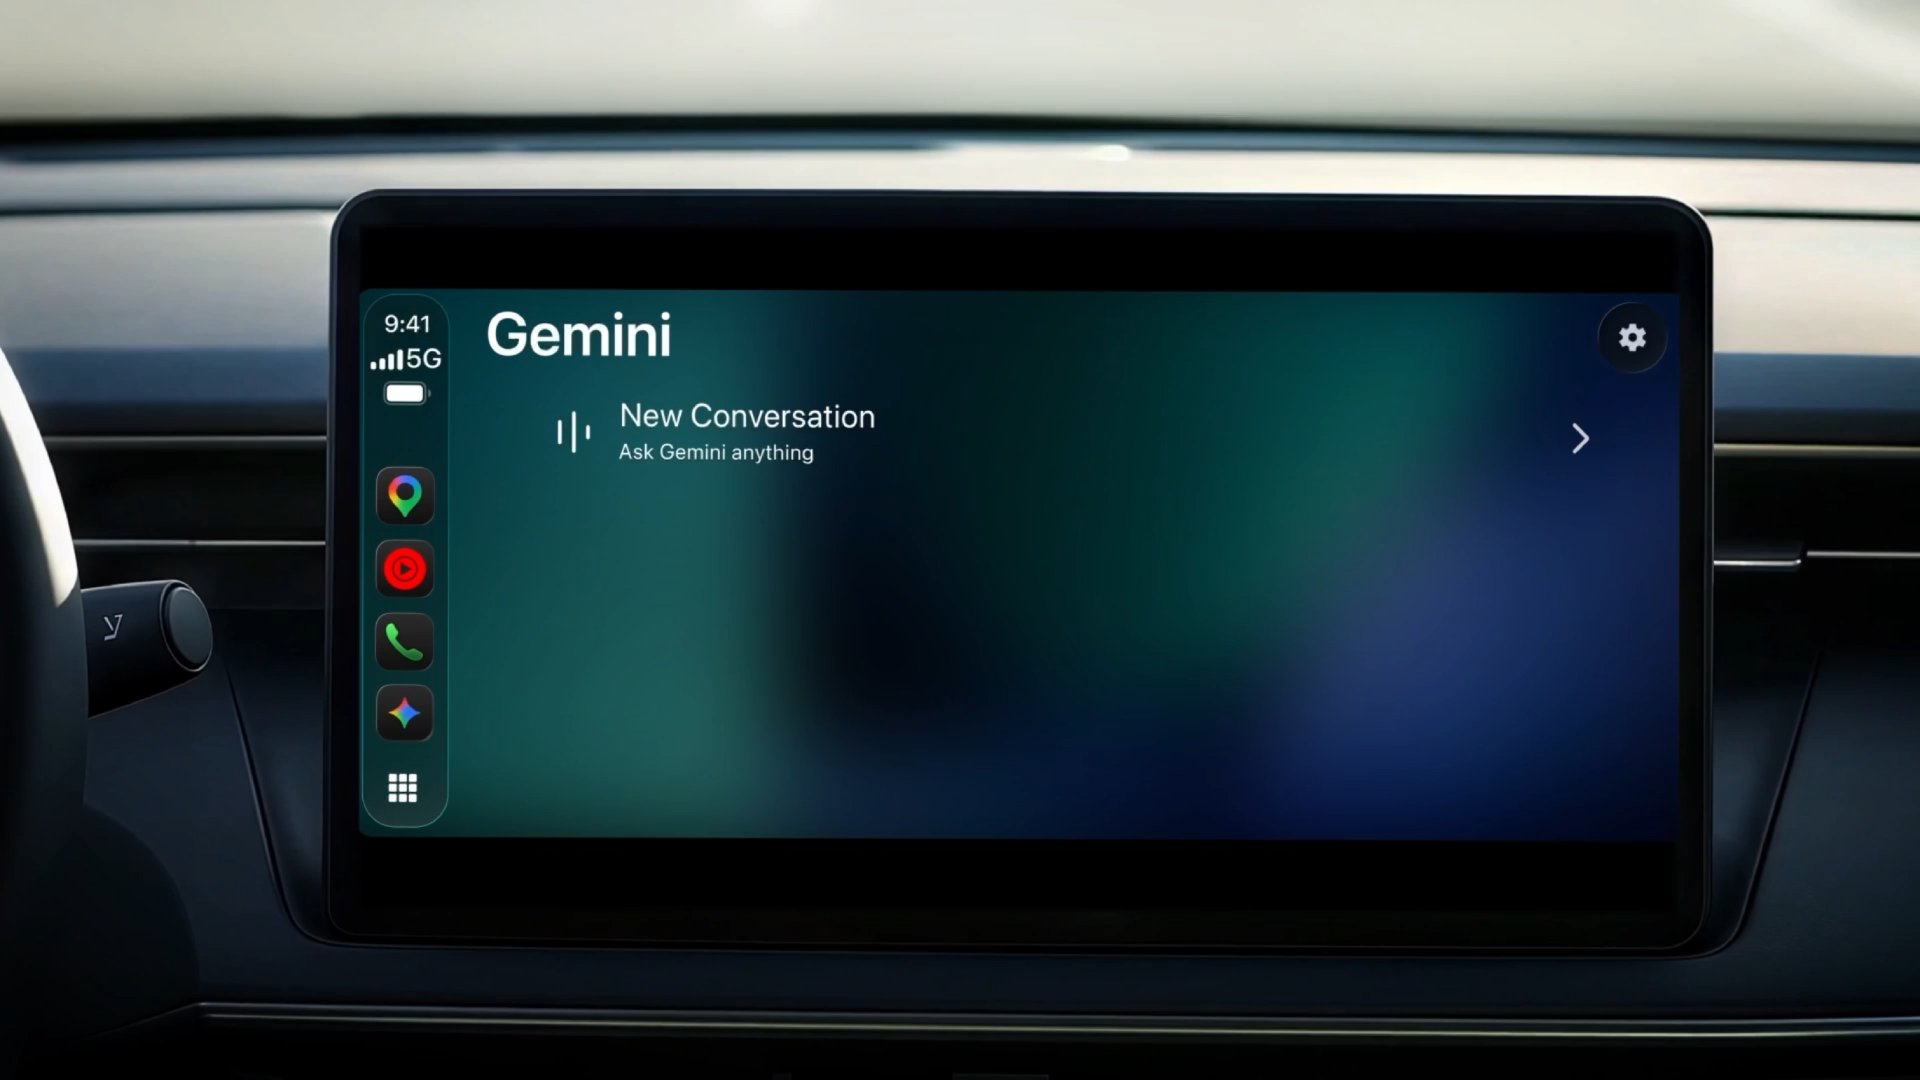
Google has announced that a dedicated Gemini app on Apple CarPlay is rolling out around the world in several languages
Read MoreA vulnerability categorized as problematic has been discovered in Dell OpenManage Ansible Modules up to 10.0.3. The impacted element is
Read More
An update that solves 16 vulnerabilities can now be installed.LinuxSecurity – Security AdvisoriesRead More
Read MoreA vulnerability identified as problematic has been detected in OpenJS Foundation Node.js up to 22.23.4/24.22.2/26.13.0. This affects the function zlib.params
Read More