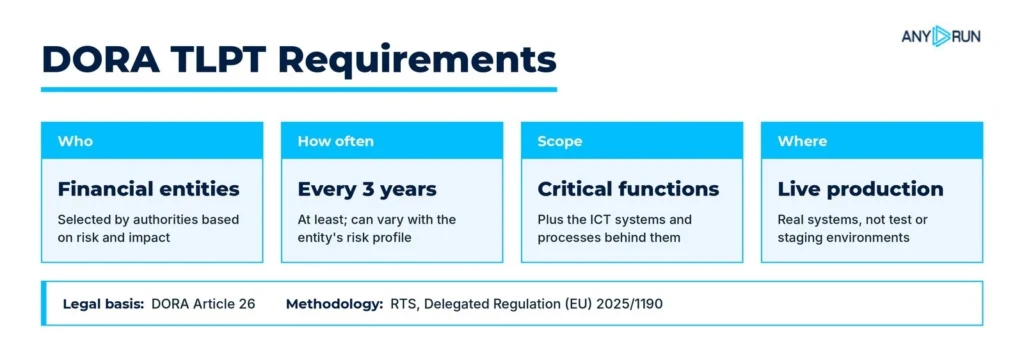
DORA TLPT Requirements Explained: Where Threat Intelligence Fits
The DORA TLPT requirements push selected EU financial entities beyond standard penetration testing. TLPT must be based on realistic threat
Read More03
The DORA TLPT requirements push selected EU financial entities beyond standard penetration testing. TLPT must be based on realistic threat
Read MoreA vulnerability labeled as problematic has been found in liedekef Events Made Easy Plugin up to 3.2.22 on WordPress. Affected
Read MoreA vulnerability marked as problematic has been reported in paoltaia GeoDirectory Plugin up to 2.8.191 on WordPress. Affected by this
Read MoreA vulnerability described as problematic has been identified in softaculous GoSMTP Pro Plugin up to 1.2.3 on WordPress. This affects
Read MoreA vulnerability classified as problematic has been found in Nord Security NordVPN up to 8.11. This vulnerability affects the function
Read MoreA vulnerability classified as problematic was found in Checkmk up to 2.2.0/2.3.0p50/2.4.0p37/2.5.0p14. This issue affects some unknown processing of the
Read MoreA vulnerability, which was classified as critical, has been found in ikus-soft Rdiffweb up to 7.1.0. Impacted is the function
Read MoreA vulnerability, which was classified as critical, was found in Ikus-soft Rdiffweb up to 2.10.5. The affected element is an
Read More
Incorrect Authorization vulnerability (CVE-2026-106030) has been found in NordVPN software.CERT PolskaRead More
Read MoreA vulnerability, which was classified as critical, was found in manuelgalan Vulnity Security Plugin up to 1.4.3 on WordPress. Impacted
Read More