CVE-2026-117627 | Red Hat Keycloak/Single Sign-On keycloak-services improper authorization
A vulnerability, which was classified as critical, was found in Red Hat Keycloak and Single Sign-On. Affected by this vulnerability
Read More03
A vulnerability, which was classified as critical, was found in Red Hat Keycloak and Single Sign-On. Affected by this vulnerability
Read MoreA vulnerability has been found in Red Hat Keycloak Single Sign-On and classified as critical. Affected by this issue is
Read MoreA vulnerability was found in Red Hat Directory Server and Enterprise Linux and classified as critical. This affects an unknown
Read MoreA vulnerability was found in Red Hat Keycloak. It has been classified as problematic. This vulnerability affects unknown code of
Read MoreA vulnerability was found in Red Hat Keycloak. It has been declared as critical. This issue affects some unknown processing
Read More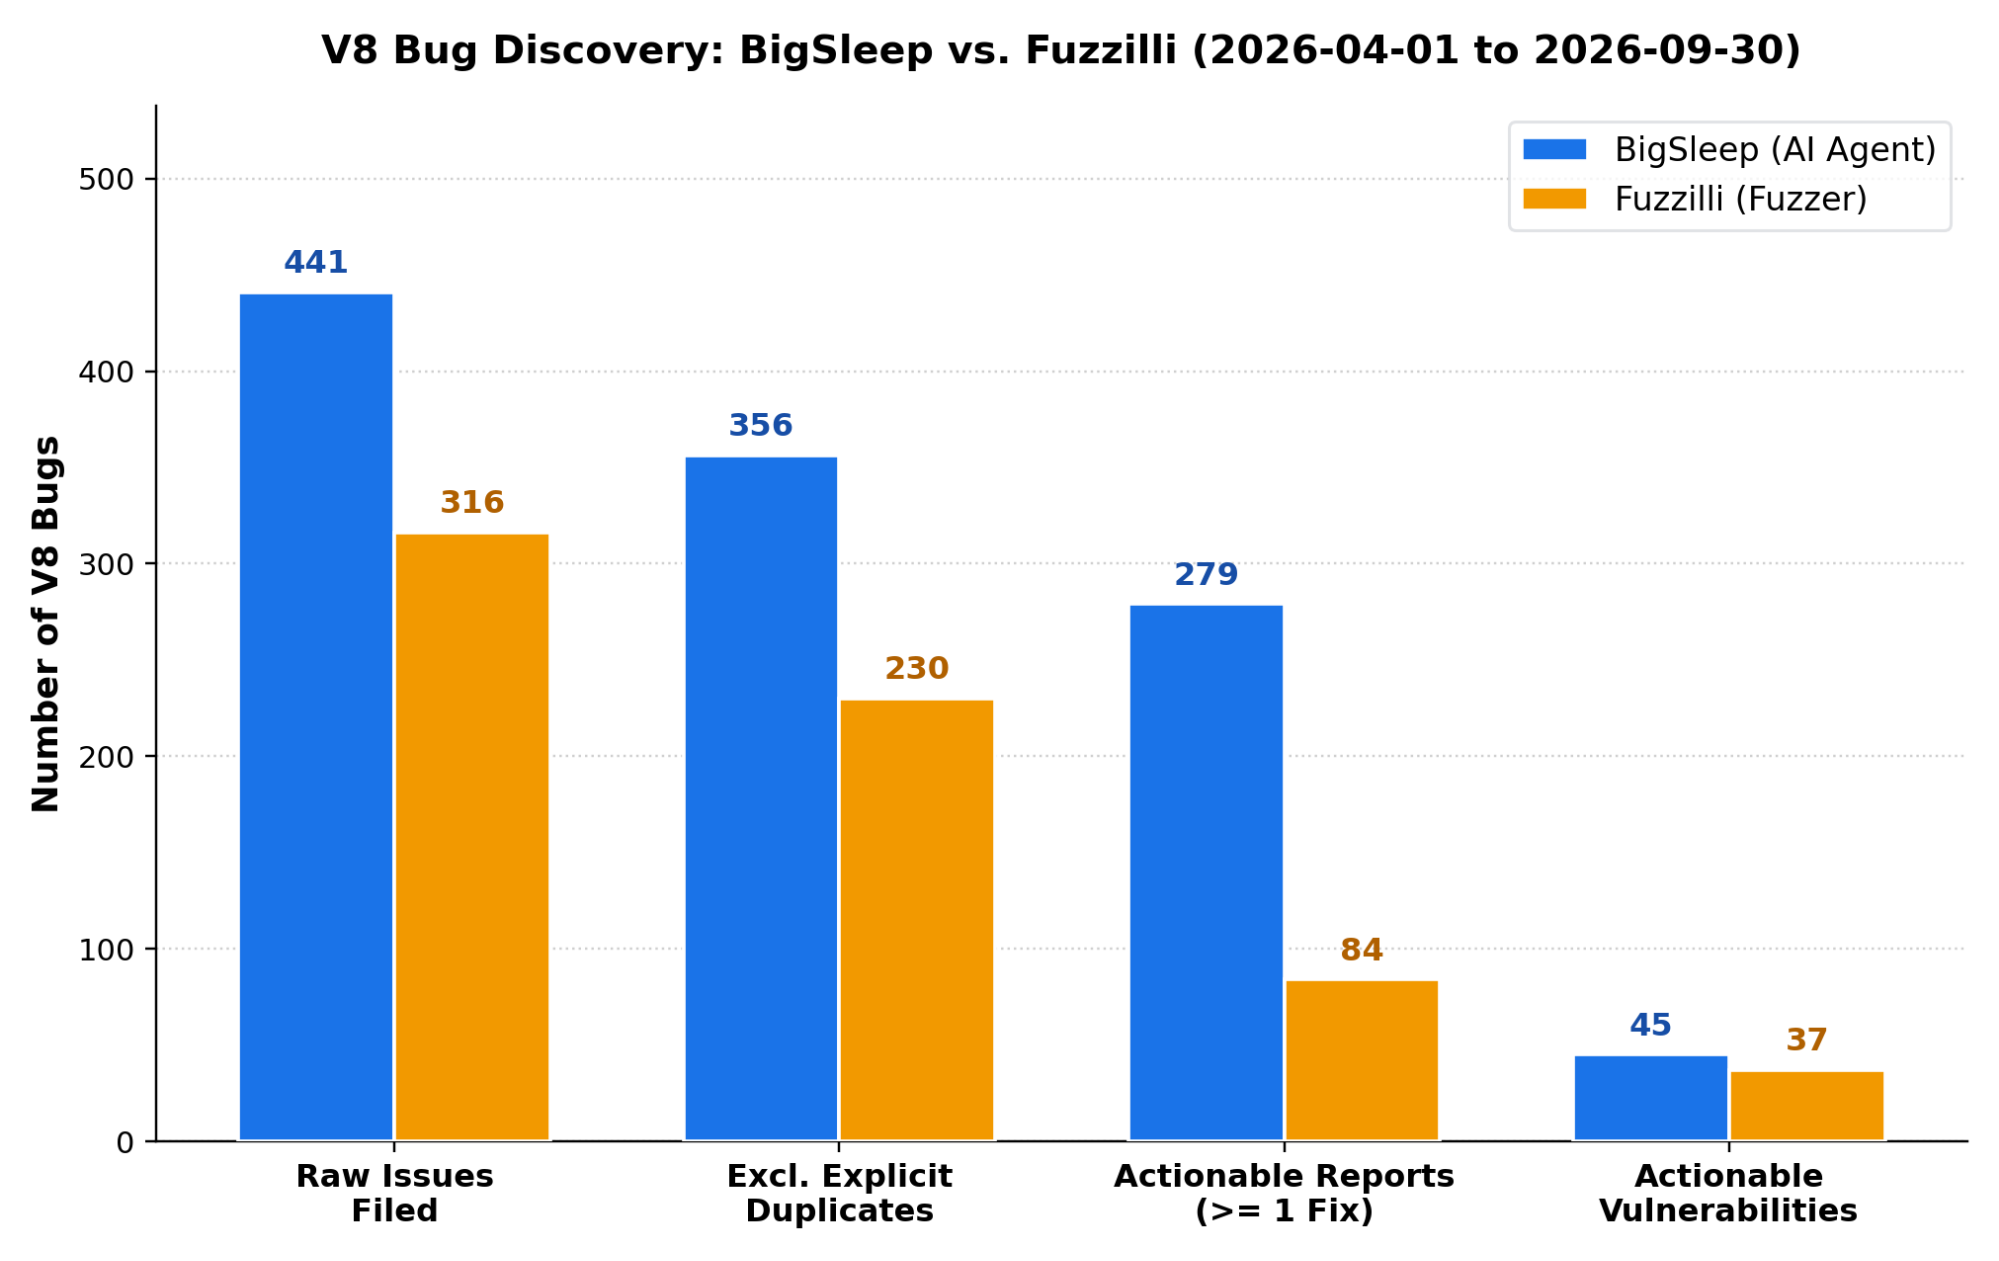
Summary Project Zero compared two automated tools used by Google to find vulnerabilities in Chrome’s JavaScript engine, V8, on a
Read MoreA vulnerability classified as problematic has been found in nvm-sh nvm up to 0.40.5. This affects the function nvm_ls of
Read MoreA vulnerability, which was classified as problematic, has been found in Octopus Deploy Octopus Server up to 2026.2.13486/2026.3.15908. Affected by
Read MoreA vulnerability, which was classified as problematic, was found in Frangoteam 1.3.2-2809. This affects an unknown part of the file
Read MoreA vulnerability has been found in Frangoteam FUXA 1.3.2-2809 and classified as critical. This vulnerability affects unknown code of the
Read More