CVE-2026-68493 | Nextcloud Server up to 34.0.0 privileges management
A vulnerability, which was classified as problematic, was found in Nextcloud Server up to 34.0.0. This affects an unknown part.
Read More03
A vulnerability, which was classified as problematic, was found in Nextcloud Server up to 34.0.0. This affects an unknown part.
Read MoreA vulnerability has been found in batiste django-page-cms up to 2.0.13 and classified as problematic. This vulnerability affects unknown code
Read More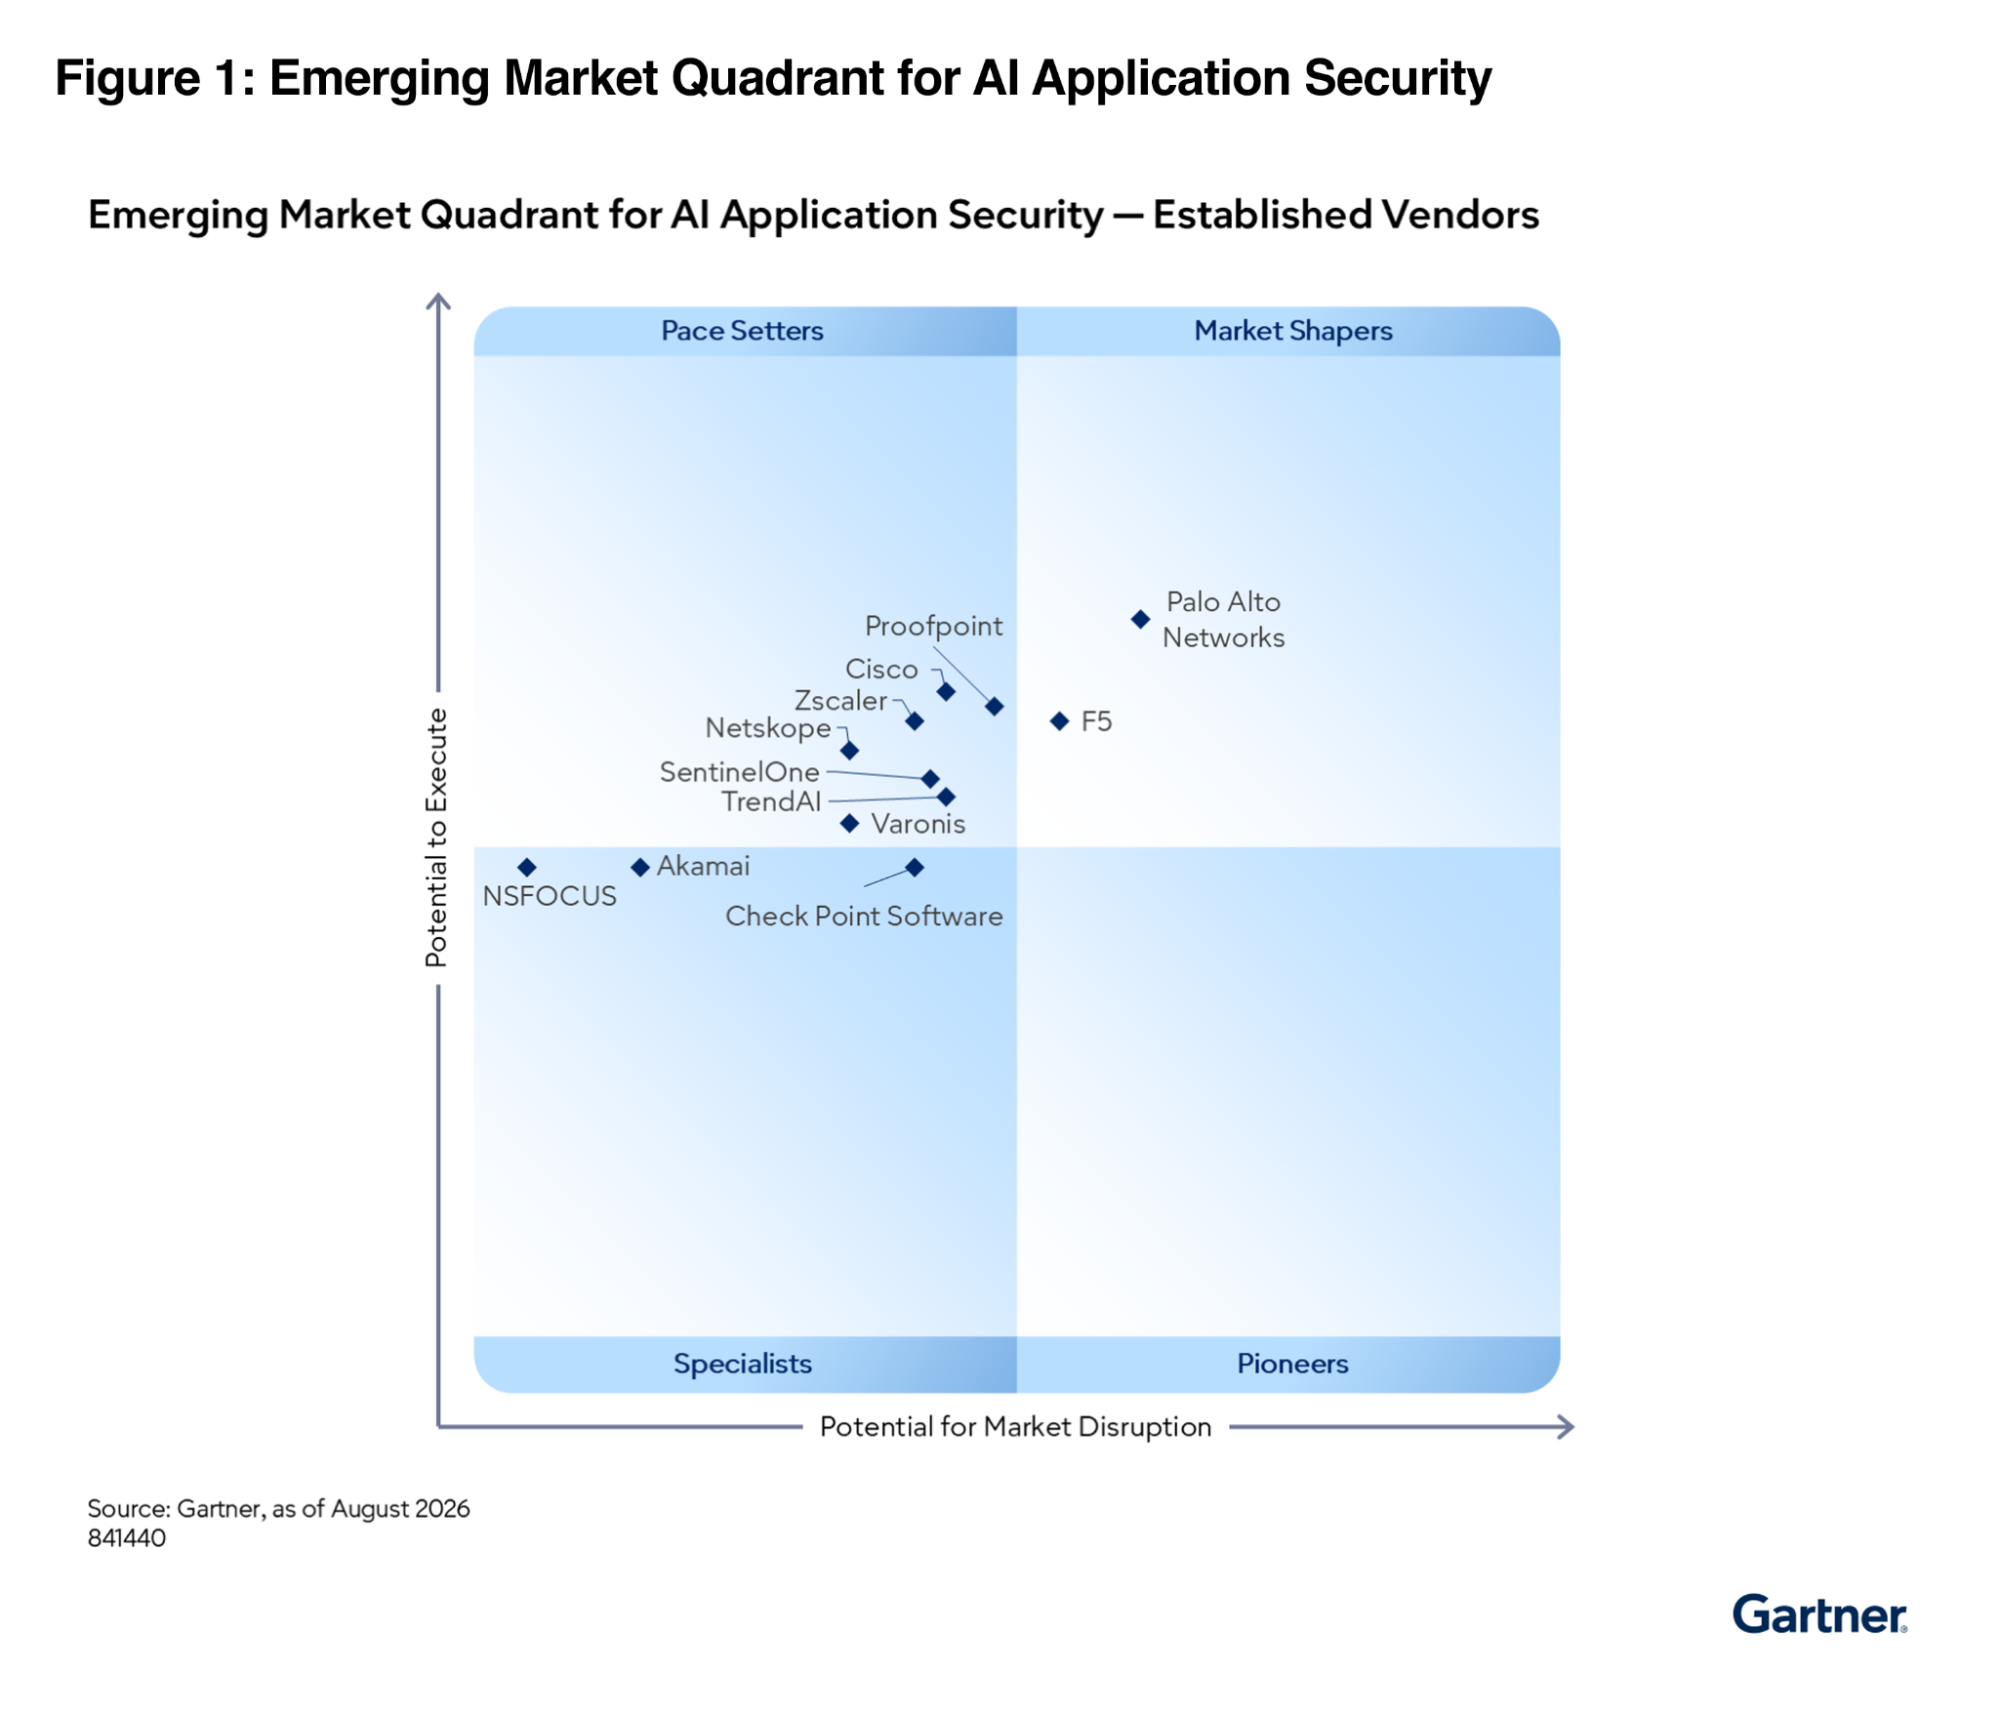
Palo Alto Networks Named a Market Shaper in 2026 September Gartner® Emerging Market Quadrant for AI Application Security — Established
Read MoreA vulnerability labeled as problematic has been found in CubeCart up to 6.7.4. This impacts an unknown function of the
Read MoreA vulnerability marked as problematic has been reported in CubeCart up to 6.7.4. Affected is the function _errorMessage of the
Read MoreA vulnerability described as problematic has been identified in CubeCart up to 6.7.4. Affected by this vulnerability is an unknown
Read MoreA vulnerability classified as problematic has been found in CubeCart up to 6.7.4. Affected by this issue is some unknown
Read MoreA vulnerability classified as problematic was found in CubeCart up to 6.7.4. This affects an unknown part of the file
Read MoreA vulnerability, which was classified as problematic, has been found in CubeCart up to 6.7.4. This vulnerability affects unknown code
Read MoreA vulnerability, which was classified as problematic, was found in CubeCart up to 6.7.4. This issue affects the function reset_id/delete_card
Read More