CVE-2026-58663 | Apache IoTDB up to 2.0.10 Thrift RPC Service improper authentication
A vulnerability was found in Apache IoTDB up to 2.0.10. It has been rated as critical. The impacted element is
Read More03
A vulnerability was found in Apache IoTDB up to 2.0.10. It has been rated as critical. The impacted element is
Read More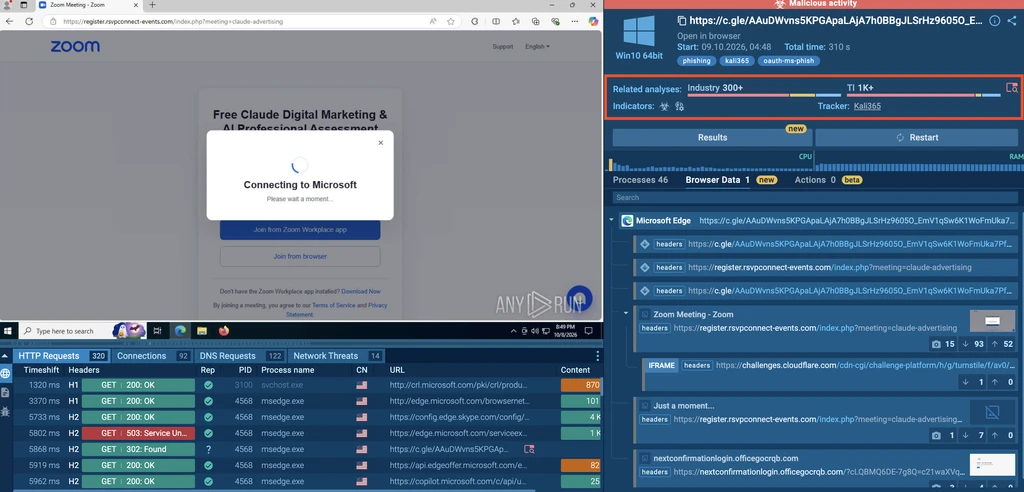
During triage, analysts may overlook valuable threat intelligence simply because they don’t know it exists. Previous investigations, related malicious activity,
Read MoreA vulnerability labeled as critical has been found in lm-evaluation-harness. Affected by this issue is some unknown functionality. Such manipulation
Read MoreA vulnerability marked as problematic has been reported in Eclipse OpenJ9 up to 0.62. This affects the function MessageBuffer::computeRequiredCapacity of
Read MoreA vulnerability described as critical has been identified in Eclipse OpenJ9 up to 0.62. This vulnerability affects the function DataDescriptor::getPayloadSize/DataDescriptor::getNextDescriptor
Read MoreA vulnerability classified as problematic has been found in WP Chill Strong Testimonials Plugin up to 3.3.12 on WordPress. This
Read MoreA vulnerability classified as problematic was found in Kevin Stover Ninja Forms Plugin up to 3.15.5 on WordPress. Impacted is
Read MoreA vulnerability, which was classified as critical, has been found in Eclipse OpenJ9 up to 0.62. The affected element is
Read MoreA vulnerability, which was classified as problematic, was found in Red Hat Advanced Cluster Security, Ansible Automation Platform, Build of
Read MoreA vulnerability has been found in HarnessRouter up to 0.31.10 and classified as problematic. This affects an unknown function of
Read More