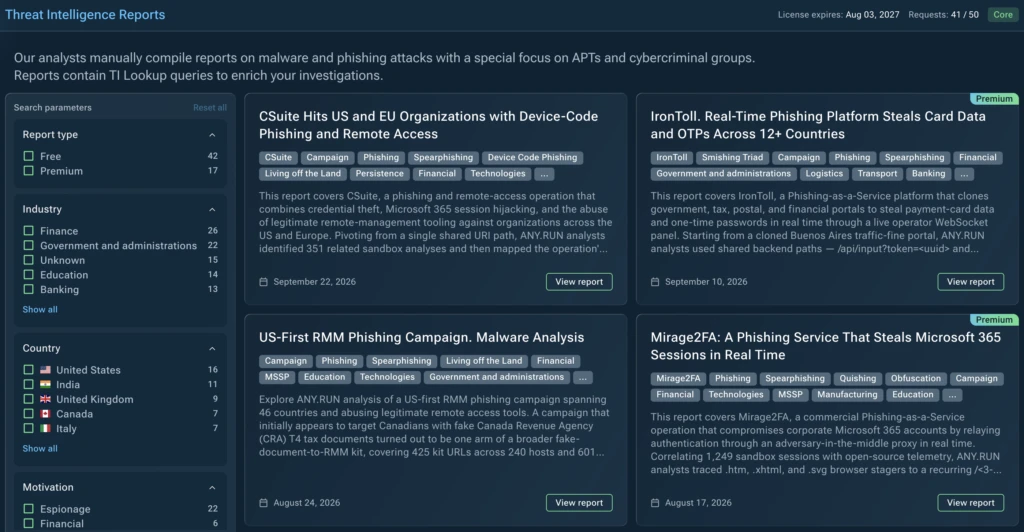
Threat Coverage Digest: New Malware Reports and 1,100+ Detection Rules
September saw an expansion of detection coverage across network, file, and behavioral activity, providing analysts with additional visibility into suspicious activity. ANY.RUN added 76 behavior signatures, 16 YARA detections, and 1,098 Suricata rules, strengthening coverage across malware activity, suspicious files, and network communications. These updates provide SOC and MSSP teams with additional evidence during investigations,
The post Threat Coverage Digest: New Malware Reports and 1,100+ Detection Rules appeared first on ANY.RUN’s Cybersecurity Blog.ANY.RUN’s Cybersecurity BlogRead More