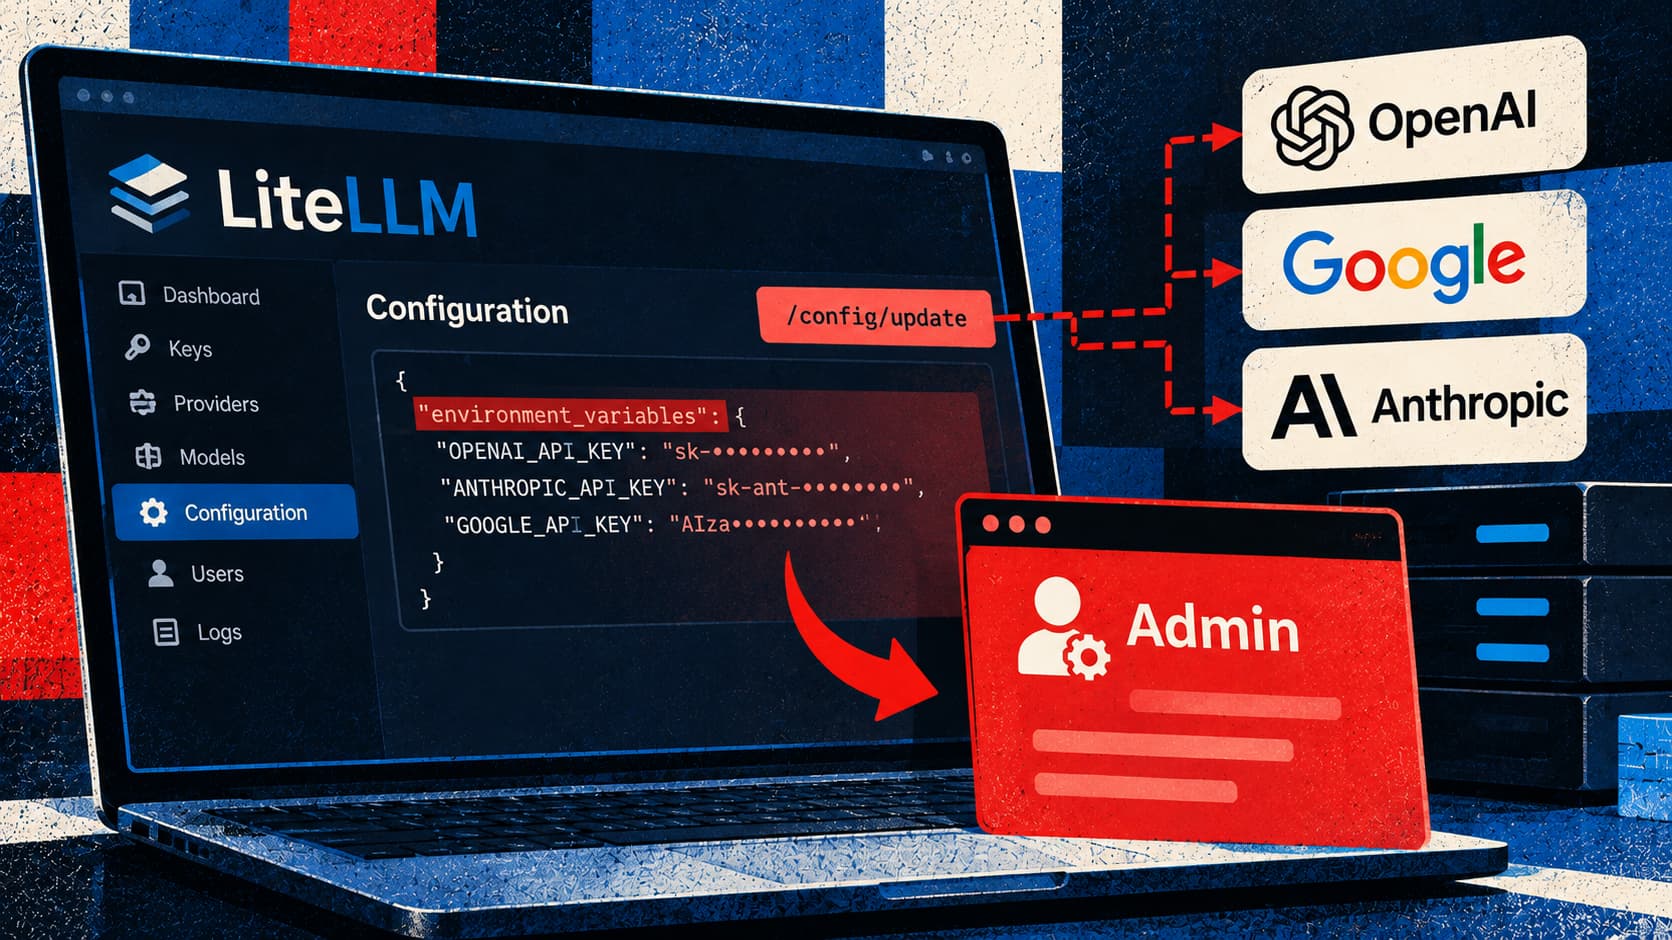
Check Point Reports LiteLLM Flaws Enabling Admin Takeover and API Key Theft
Check Point Research found two LiteLLM vulnerabilities that could let low-privilege users execute code, access sensitive files, hijack admin accounts, and steal AI provider API keys.Hackread – Cybersecurity News, Data Breaches, AI and MoreRead More