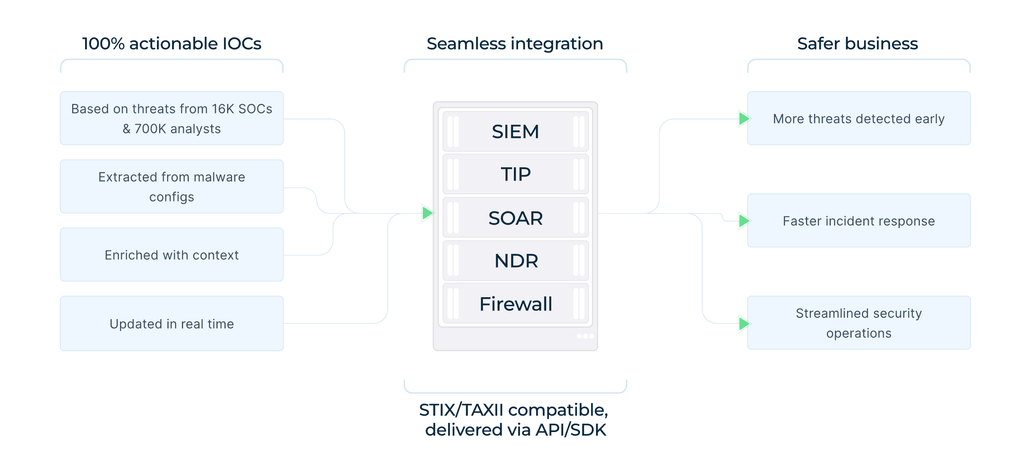
Cyber Threat Context for Early Response: Enriching SOC Telemetry with Real-Time Intel from 16K Organizations
When an IOC hits the SOC, the clock is already running. An IP address, domain, file hash, or suspicious URL can trigger a detection, but an analyst still needs to understand what it is, whether it is connected to known malicious activity, and what happened around it. The longer it takes to build that context,
The post Cyber Threat Context for Early Response: Enriching SOC Telemetry with Real-Time Intel from 16K Organizations appeared first on ANY.RUN’s Cybersecurity Blog.ANY.RUN’s Cybersecurity BlogRead More