Your Threat Intelligence Stack Has Blind Spots. Here’s How to Close Them
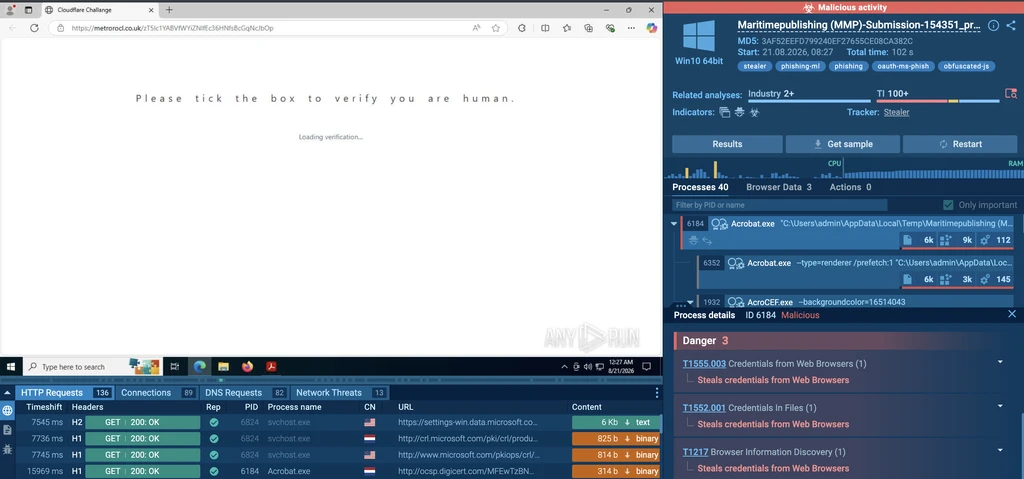
Your SOC pays for multiple threat intelligence feeds, yet fresh malicious domains and IPs can still appear in telemetry as unknown. When feeds rely on overlapping sources, more subscriptions may deliver the same indicators while leaving emerging threats uncovered. Analysts must fill these gaps manually, checking indicator reputations, comparing sources, and gathering evidence. Every extra
The post Your Threat Intelligence Stack Has Blind Spots. Here’s How to Close Them appeared first on ANY.RUN’s Cybersecurity Blog.ANY.RUN’s Cybersecurity BlogRead More